

Table of Contents
Don't have the time to read the entire post? Our human writers will be sad, but we understand. Summarize the post with your preferred LLM here instead.
The top Firebase Authentication alternatives for 2026 are Descope, Supabase, Keycloak, Amazon Cognito, and Microsoft Entra External ID, each suited to a different need. Firebase Authentication is a go-to identity solution for developers building on Google Cloud, especially for mobile-first or early-stage applications. However, as apps grow in complexity and scale, teams find themselves constrained by its limitations and look for alternatives that offer more control over cost, data, and identity features, without being tied to a single cloud provider.
In particular, vendor lock-in, limited backend flexibility, cost and scalability concerns, data privacy needs, and other issues often push developers to look for Firebase Auth alternatives that offer greater customization, better cost control, and true enterprise-grade features.
In this guide, we’ll cover:
Why developers seek out Firebase Auth alternatives
What the top Firebase Auth alternatives have to offer
How to pick the best Firebase Auth for your needs
At a glance
The top Firebase Authentication alternatives for 2026 are Descope, Supabase, Keycloak, Amazon Cognito, and Microsoft Entra External ID.
Developers look beyond Firebase Auth mainly to avoid Google vendor lock-in, as well as for more control over cost, data, and identity features.
Descope leads for teams that want to add and change auth through visual workflows without writing custom code, with passkeys, MFA, and AI agent authentication built in.
Supabase and Keycloak are the strongest open-source and self-hosted options, while Amazon Cognito and Microsoft Entra External ID suit AWS and Microsoft-aligned teams.
The right choice depends on whether you want a managed platform, an open-source option, or an ecosystem-native service, and on your developer experience and compliance needs.
Quick facts
What Firebase Auth is | Google’s managed authentication service, built into Firebase and tightly coupled to Google Cloud |
Why developers seek alternatives | Vendor lock-in, cost and scalability concerns, data privacy needs, and limited customization |
Top alternatives | Descope, Supabase, Keycloak, Amazon Cognito, and Microsoft Entra External ID |
Open-source options | Supabase and Keycloak, both self-hostable with no licensing costs |
Key consideration | Whether you want a managed platform, an open-source option, or an ecosystem-native service |
Why developers seek Firebase Auth alternatives
Avoiding Google vendor lock-in is the single biggest reason developers look for a Firebase Auth alternative. Many teams outgrow Firebase Authentication for a few key reasons:
Vendor lock-in: Firebase is tightly integrated with Google Cloud services, making it difficult to migrate to other platforms without major architectural changes.
Cost and scalability: Firebase’s usage-based pricing can result in unpredictable cost spikes, especially for high-traffic or global applications.
Data privacy and control: User data is stored on Google’s infrastructure by default, which can make it harder to meet strict compliance requirements such as GDPR or HIPAA.
Limited customization and infrastructure control: Firebase offers minimal flexibility for teams that want to self-host, support hybrid environments, or build multi-tenant and partner-specific auth flows.
Security and compliance concerns: Firebase relies on basic security defaults and lacks built-in tools for advanced security orchestration, leaving room for misconfigurations that could expose user data.
Each option below is a popular Firebase Authentication alternative, but they differ in strengths depending on your technical requirements and product roadmap.
Firebase Auth alternatives at a glance
Here’s how the top Firebase Auth alternatives compare:
Key capabilities | Developer experience | Open source | Strengths | Ideal for | |
|---|---|---|---|---|---|
Descope | Flexible auth support, connector ecosystem, strong multi-tenancy, AI and agentic support | No-code and low-code visual workflows, SDKs, APIs, MCP server and skills | No | Visual workflows, predictable pricing, self-service SSO and SCIM, adaptive MFA | Devs building cross-platform, multi-tenant, or agent-ready apps |
Supabase | Many auth options, row-level security, serverless functions, flexible SDKs | Firebase-like APIs and SDKs, dashboard-driven setup | Yes | Open-source and self-hostable, Postgres integration, Firebase-like UX | Devs and startups seeking a stack like Firebase with more backend control |
Keycloak | Self-hosting, built-in admin console, fully customizable UX, protocol flexibility | Admin console-driven, steeper setup curve | Yes | Full auth control, protocol flexibility, open-source with vendor neutrality | Orgs with DevOps resources that want to self-host auth and need customization |
Amazon Cognito | User pools, federated ID support, AWS triggers for auth flow customization | AWS-native tooling, Lambda-driven customization | No | Deep AWS integration, flexible federation options, custom auth logic | AWS-invested teams that need flexible ID federation and are OK with complexity |
Microsoft Entra External ID | Self-service, branded user journeys, built-in security, strong user lifecycle management | Azure-native tooling, policy-driven configuration | No | Enterprise alignment, compliance-ready, user ID governance functionalities | Orgs that already use MS infrastructure and need enterprise ID management tools |
Below, we’ll take a closer look at how each platform works and their optimal use cases.
Descope
Overview
Descope is a modern external IAM platform designed for developers who need flexible, secure authentication without the overhead of managing complex infrastructure. It’s ideal for both B2C and B2B SaaS apps, especially those that need built-in support for multi-tenancy, partner integrations, or IAM for AI agents and MCP ecosystems.
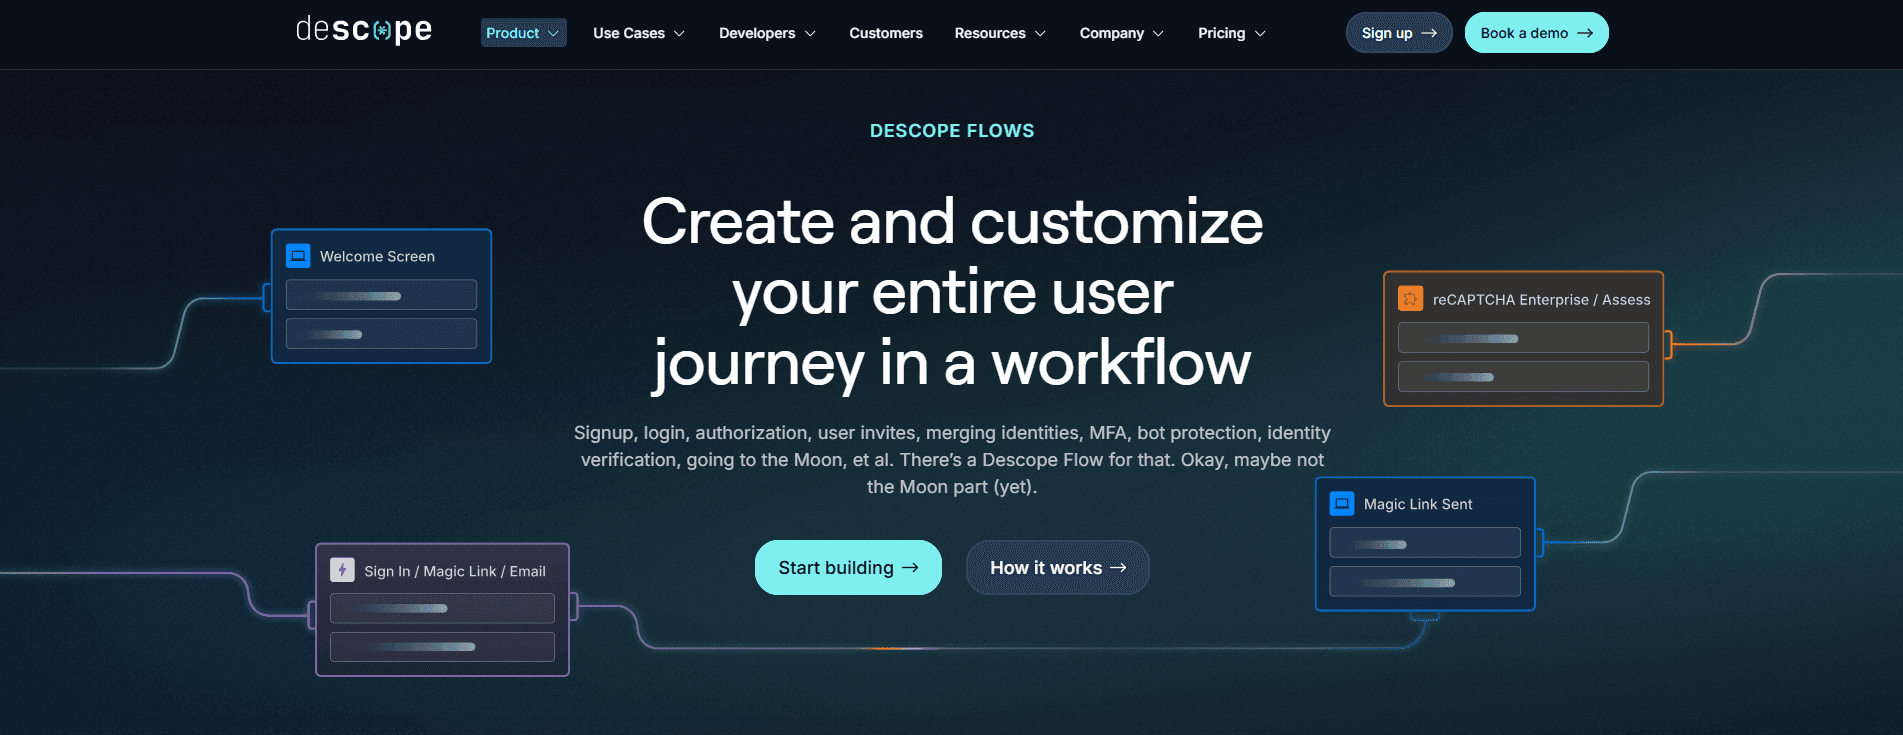
Descope includes native features like organization management, tenant-aware SSO, and fine-grained access controls, making it easy to scale across users and environments. In addition, it enables teams to ensure secure, scoped, and consented access for their AI agents and MCP servers, an approach industry analysts have called out while recognizing Descope as one of the first identity providers to treat AI agents as first-class identities.
Key capabilities
Visual workflow editor to create and modify login, signup, and MFA flows
Extensive plug and play connector ecosystem for seamless integration with third-party services
Anonymous user tracking for top-of-funnel B2C user visibility
Comprehensive SSO Setup Suite for configuring, mapping, and testing SSO and SCIM connections
Embeddable UI widgets for self-service identity management and admin
Support for a wide range of auth methods including passkeys, OTP, magic links,social login, and Google One Tap
Support for 15+ web, mobile and backend SDKs and a robust REST API
Identity orchestration that coordinates authentication, authorization, risk, and fraud tools
Agentic identity support to get agents enterprise-ready and organizations agent-ready
Firebase integration made easy
Developers may not want to move away from Firebase Authentication completely, but still seek more robust capabilities to customize login, MFA, or user onboarding. By acting as a federated identity provider via OpenID Connect, Descope handles the user authentication flow, then passes the authenticated user to Firebase. This setup adds flexibility without losing Firebase’s core capabilities.
Descope also lets you add passkey authentication to your Firebase app by acting as an OIDC identity provider. It handles the full passkey login flow and sends the authenticated user to Firebase, enabling secure, passwordless login without changing your backend.
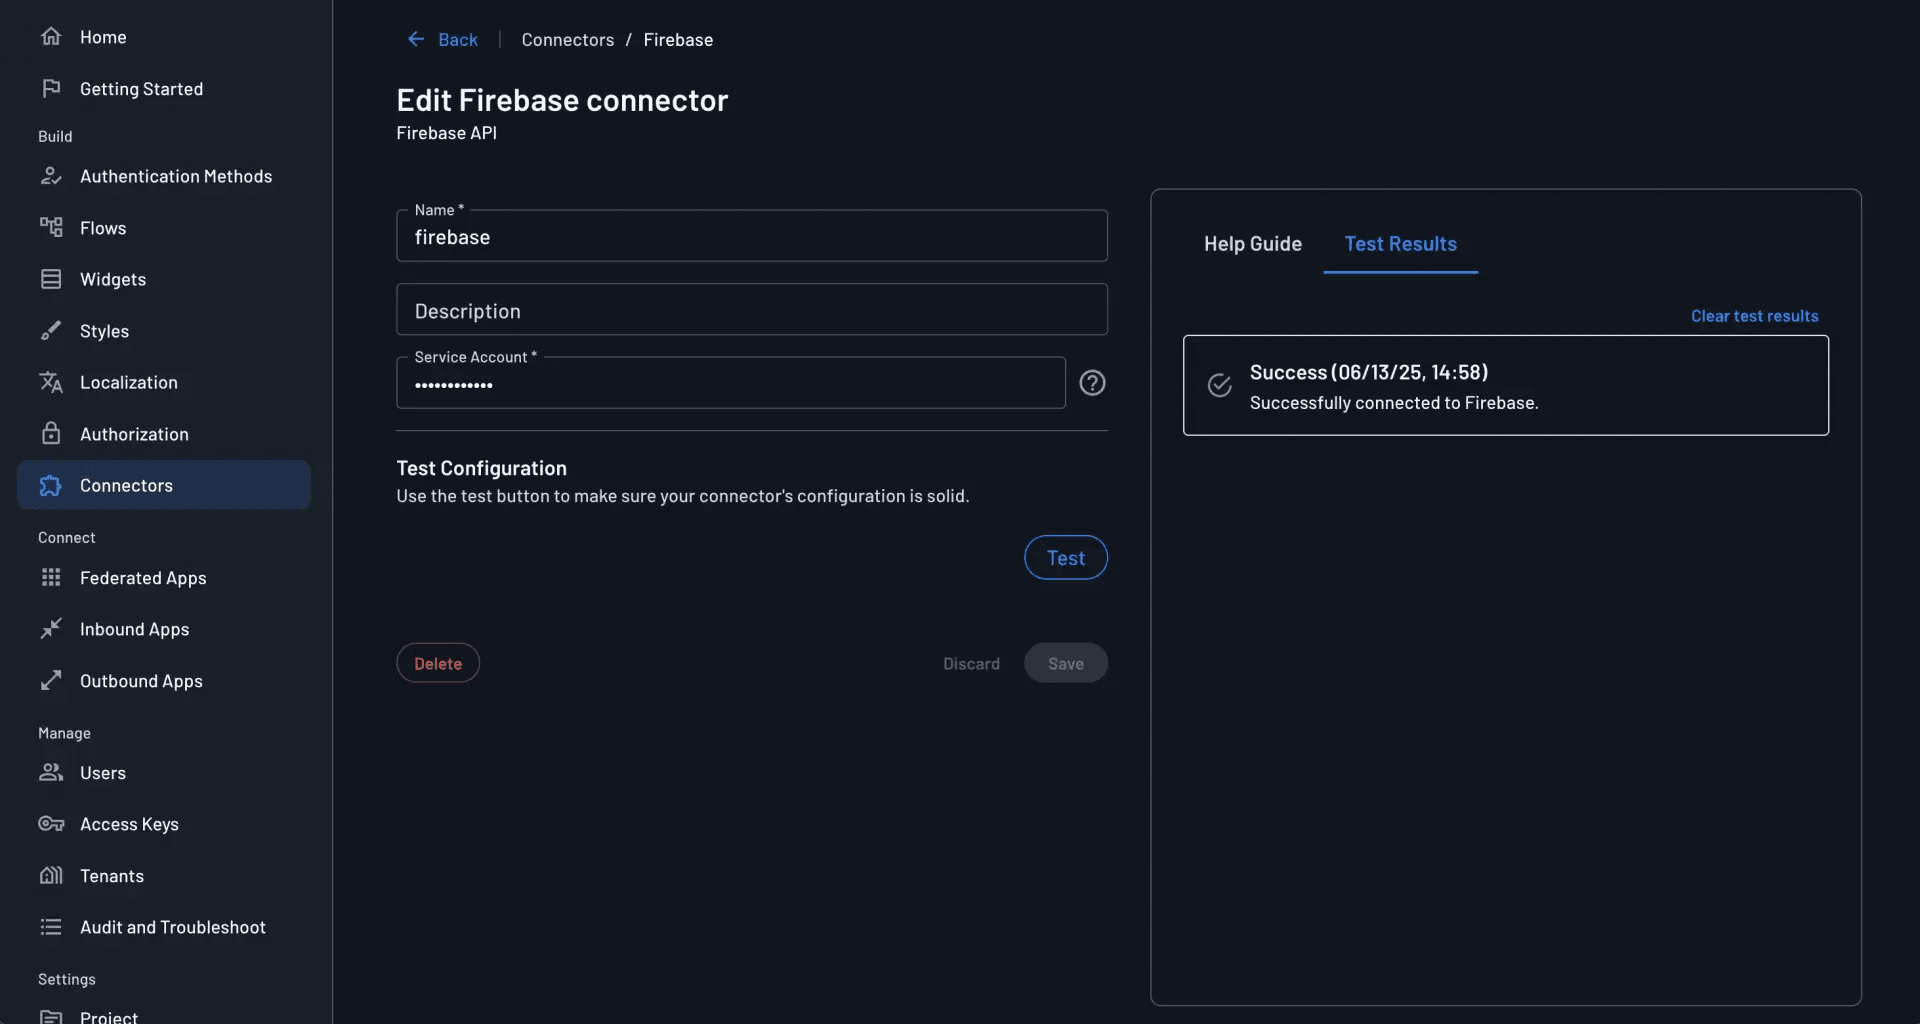
Moreover, Descope provides a Firebase Connector that lets you use Descope authentication without moving your product off Firebase. With this integration, Descope can return a Firebase-compatible token as part of the authentication response—available through SDKs or API.
Strengths
Visual workflows: Descope’s drag and drop editor lets developers design login, signup, MFA, and SSO flows without backend scripting or custom glue code. This simplifies auth implementation and speeds up time to production.
Predictable pricing and responsive support: Descope offers transparent, usage-based pricing with no hidden fees or surprise jumps. Teams benefit from fast, knowledgeable support to help them implement, troubleshoot, and scale with confidence, as evidenced by Descope winning the Best Support G2 badge the last eight quarters in a row.
Streamlined SSO: Build and manage SSO journeys with workflows, enable self-service setup, and migrate existing configurations with no disruption.
Passwordless authentication: Descope supports passkeys, magic links, OTP, and social login natively. These methods can be easily added to any flow, reducing reliance on passwords while improving UX and security.
Omnichannel authentication: With Descope, authentication flows can be unified across web, mobile, and third-party or partner applications. The same no-code or low-code workflows can be reused across environments, making updates and scaling easier over time.
Adaptive MFA: Firebase Authentication’s own MFA is limited to SMS by default, with TOTP authenticator-app support only available after upgrading to the paid Identity Platform tier. Descope includes a wide range of MFA methods out of the box and lets developers enforce them only when needed, using native and third-party risk signals, without overhauling existing auth systems.
Enterprise agent ready: Descope supports secure authentication and access control for agentic AI systems through its Agentic Identity Hub.
Built for developers: Whether using hosted components or fully custom UIs, Descope gives developers flexibility with SDKs and APIs in React, Node.js, Python, Flutter, and more. The platform fits into any tech stack without locking teams into rigid patterns.
Ideal for
Developers building cross-platform, multi-tenant, or agent-ready apps who want auth flows they can launch and modify quickly without backend rewrites.
Limitations
As a newer platform than some of the legacy providers on this list, Descope has a smaller enterprise case study library, though its production customer base is growing quickly across both B2C and B2B SaaS deployments and includes customers such as GoFundMe, Databricks, Linktree, and Navan. Because Descope is a managed service rather than something you self-host, teams that specifically want to run their own auth infrastructure on their own servers will find Keycloak or self-hosted Supabase a closer fit.
Supabase
Overview
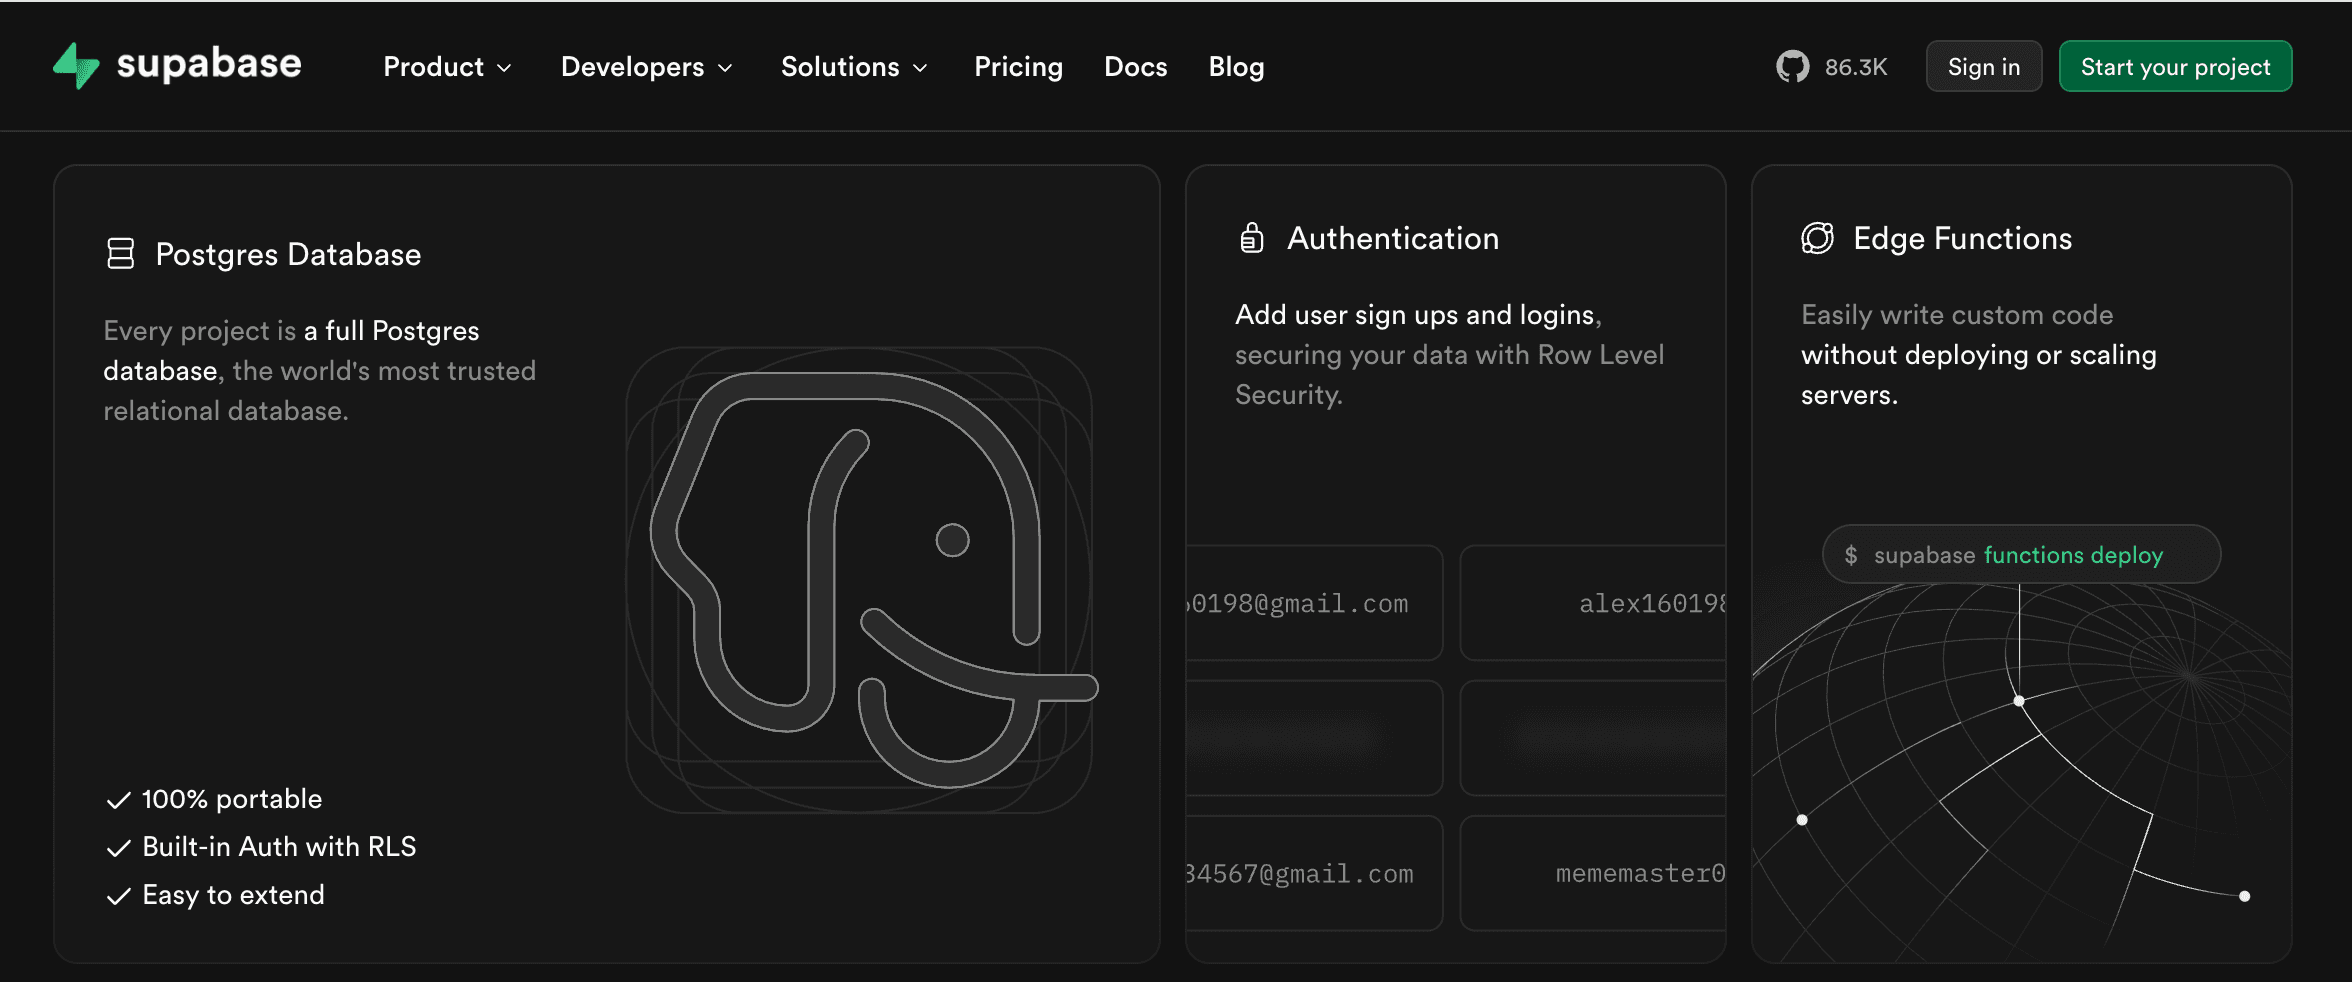
Supabase is an open-source Firebase alternative that offers a backend-as-a-service experience with built-in authentication, Postgres database, storage, and edge functions. Its authentication service is powered by GoTrue, a JWT-based auth server, and supports multiple login methods out of the box. Supabase is a good choice for developers who want Firebase-like functionality with more transparency and control.
Key capabilities
Email/password, magic link, and third-party OAuth providers
Postgres-based auth with row-level security
Serverless functions (Edge Functions) for backend logic
SDKs for JavaScript, Flutter, and other platforms
Self-hosted or fully managed deployment options
Support for asymmetric JWT signing, with P-256 elliptic curve and RS256 options
Strengths
Open-source and self-hostable: Supabase allows full control over the backend and can be deployed on your own infrastructure.
Tight integration with Postgres: Offers fine-grained access control and real-time capabilities using native Postgres features.
Firebase-like developer experience: Provides an easy transition for teams familiar with Firebase but looking for open standards and flexibility.
Ideal for
Developers and startups that want a Firebase-style stack with more backend control and the ability to self-host if needed.
Limitations
Authentication is one part of a broader backend platform for Supabase, so advanced identity features like fine-grained multi-tenancy or enterprise SSO orchestration are less deep than what a dedicated identity provider offers. Self-hosting adds operational work too: teams running their own GoTrue instance lose access to some dashboard-managed OAuth provider settings and take on responsibility for upgrades, backups, and scaling that a managed platform would otherwise handle.
Keycloak
Overview
Keycloak is an open-source identity and access management solution built by Red Hat. Unlike Firebase Authentication, which is a hosted, simplified solution tied to Google Cloud, Keycloak gives developers full control over their auth infrastructure. It’s designed for teams that want to self-host and customize every part of their login and identity flows.
Key capabilities
Self-hosted deployments with support for clustering and high availability
Built-in admin console to manage users, roles, and authentication realms
Customizable login screens and authentication flows
Native support for standard protocols including SAML, OIDC, and LDAP
Fine-grained role-based and attribute-based access control
Step-up authentication support extended to SAML service providers (in early preview), alongside existing OIDC support
Strengths
Full control over authentication stack: Unlike Firebase, Keycloak allows teams to deeply customize their identity setup, including user journeys, token lifetimes, and login screens.
Protocol flexibility: Supports enterprise standards like SAML and LDAP out of the box—protocols not natively supported by Firebase Auth.
Open-source and vendor-neutral: Can be deployed in any environment with no licensing costs, offering more long-term flexibility than Firebase’s Google Cloud lock-in.
Ideal for
Organizations with DevOps resources that want to self-host authentication and need maximum flexibility around protocols, customization, and integration with legacy systems.
Limitations
Keycloak is self-hosted only, so it requires dedicated DevOps resources for deployment, upgrades, and scaling, with no managed cloud option from the maintainers to fall back on. Teams without existing platform engineering capacity often underestimate the ongoing maintenance burden until they’re a few releases in.
Also read: Top 6 Keycloak Alternatives
Amazon Cognito
Overview
Amazon Cognito is AWS’s native authentication and user management service, offering secure access control for web and mobile apps. Like Firebase Authentication, it provides built-in support for user sign-up, login, and federated identity. However, while Firebase emphasizes simplicity and fast setup, Cognito requires more AWS-specific knowledge and is better suited to teams already building within the AWS ecosystem.
Key capabilities
User pools for managing and authenticating users
Federated identity support with SAML, OIDC, and social providers
AWS Lambda triggers to customize auth flows
Native integration with AWS services like API Gateway, AppSync, and IAM
Multi-Region replication for authentication resilience during regional outages
Self-service, on-demand provisioned API rate limits
Strengths
Deep AWS integration: Works seamlessly with other AWS services, making it ideal for applications already running on the AWS stack.
Flexible federation options: Supports SAML, OIDC, and major social providers, offering more identity protocol coverage than Firebase.
Custom auth logic: Developers can use Lambda triggers to inject custom behavior into sign-up, sign-in, and token issuance flows—something Firebase only supports with more limited extensibility.
Limitations
UI customization is limited compared to purpose-built CIAM platforms, multi-tenant identity needs workarounds rather than native support, and Cognito is best suited to teams already on AWS rather than those wanting a cloud-agnostic option.
Also read: The Top 5 Amazon Cognito Alternatives
Microsoft Entra External ID
Overview
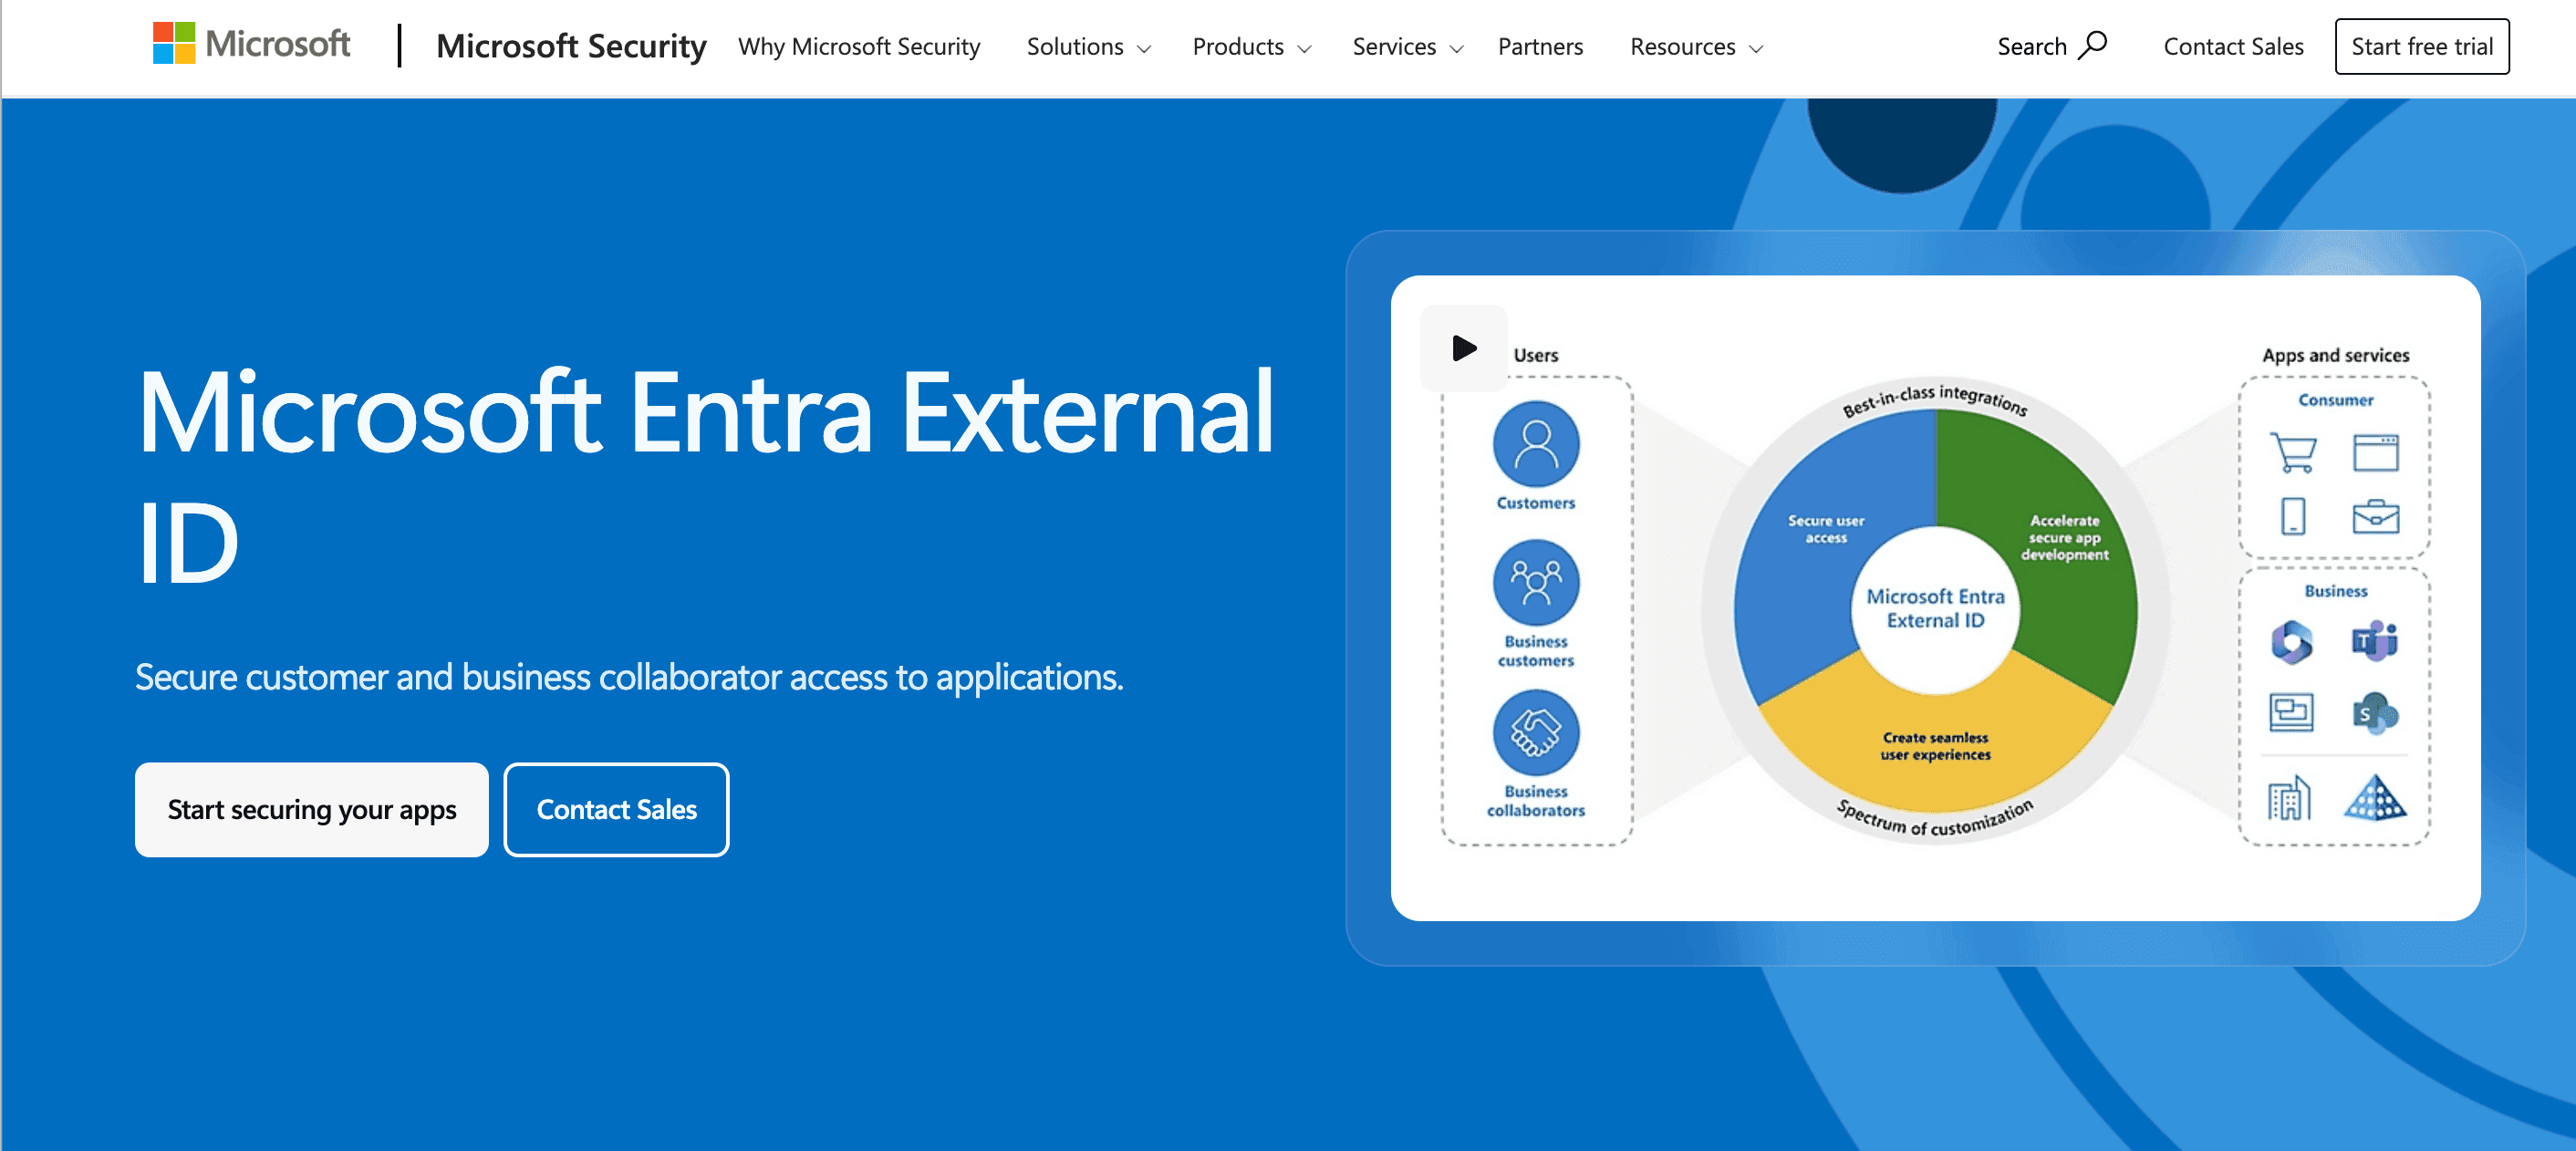
Microsoft Entra External ID is a cloud-based identity and access management service designed for enterprises that need to allow external identities to securely access their apps and resources. While Firebase Authentication focuses on quick setup and developer-friendly tools, Entra External ID is built for complex enterprise environments that require advanced security, compliance, and governance features. It offers powerful capabilities but may be harder to implement for teams not already using Microsoft infrastructure.
Key capabilities
Supports self-service registration and sign-in with social or enterprise identities
Enables branded, customizable user journeys for external apps and portals
Includes built-in security, conditional access, and MFA options
Manages user lifecycle with governance, access reviews, and expiration policies
Delegated credential management API for letting customer-facing apps manage a signed-in user’s own passkeys
Strengths
Enterprise alignment: Includes native tools for compliance, access control, and identity lifecycle management.
Compliance-ready: Works with Microsoft cloud and productivity services, making it a strong fit for existing Azure environments.
Identity governance features: Native tools for managing user lifecycle, permissions, and audit trails
Ideal for
Large organizations that already use Microsoft 365, Azure, or hybrid infrastructure and need enterprise-grade identity management and governance.
Limitations
Entra External ID is tightly coupled to the Microsoft ecosystem and less flexible for multi-cloud teams. The External ID feature set, while maturing quickly, is still newer and less complete than workforce-focused Entra ID.
How to choose the right Firebase Auth alternative
When choosing the best Firebase Auth alternative, consider your existing infrastructure, needs, and reasons for augmenting or replacing Firebase Auth.
If your priority is | Consider | Why |
|---|---|---|
Avoiding vendor lock-in | Descope, or a self-hosted option like Supabase or Keycloak | Descope gives you a managed platform not tied to a single cloud, while self-hosting gives you full infrastructure ownership |
A simple, vendor-neutral setup | Descope | Visual workflows, SDKs, and an MCP server get auth running quickly without committing to one cloud ecosystem |
Open-source flexibility and control | Supabase or Keycloak | Both are self-hostable with no licensing costs, trading operational work for full control |
Staying within an existing AWS environment | Amazon Cognito | Deep native integration with AWS services like Lambda, API Gateway, and IAM |
Staying within an existing Microsoft environment | Microsoft Entra External ID | Built-in alignment with Azure, Microsoft 365, and enterprise governance tools |
Enterprise SSO features | Descope or Microsoft Entra External ID | Both offer enterprise-ready SSO and compliance functions, with Descope spanning ecosystems and Entra External ID suited to Microsoft-aligned orgs |
Move beyond Firebase Auth with Descope
Descope gives teams a managed alternative to Firebase Auth with no vendor lock-in to a single cloud, adding login, passkeys, and MFA through SDKs and visual flows instead of custom backend code. Teams get the flexibility of a fully customizable auth system without the maintenance burden of self-hosting or the constraints of staying inside one cloud provider’s ecosystem.
Sign up for a Free Forever account with Descope and start building secure, scalable auth flows today. Have questions about augmenting or replacing Firebase? Book time with our experts.