Table of Contents
Don't have the time to read the entire post? Our human writers will be sad, but we understand. Summarize the post with your preferred LLM here instead.
FusionAuth is the solution for developers who want a full-featured identity platform that they can deploy, manage and customize. The flexibility of the deployment options and the level of configuration available is what appeals to organisations looking for a high degree of control over their identity infrastructure.
However, this level of control can introduce additional complexity. Configuring authentication flows, maintaining infrastructure, and implementing tenant-specific enterprise SSO can drain engineering resources. As applications scale and identity requirements increase, managing authentication can become a substantial time and cost burden.
For organizations looking to simplify identity management, managed authentication platforms are an alternative. They reduce the infrastructure you need to manage, simplify enterprise onboarding, and let developers bring new auth experiences to market faster.
In this guide, we explore why developers are looking for FusionAuth alternatives and compare six other identity platforms on features, flexibility, price, and the benefits of a managed authentication service.
Quick answer: what are the best FusionAuth alternatives?
Leading FusionAuth alternatives for teams seeking managed authentication include:
Descope: Managed authentication with visual workflows, multi-tenancy, self-service SSO/SCIM, and agentic identity.
Auth0: Mature identity platform with extensive integrations and developer extensibility.
Amazon Cognito: AWS-native authentication with deep cloud service integrations.
Firebase Authentication: Easy-to-deploy authentication for mobile and web applications.
Ory: Open-source, API-first identity with managed cloud deployment options.
Entra External ID: Managed customer identity with Microsoft ecosystem integration and enterprise security.
Why developers seek FusionAuth alternatives
Many teams outgrow FusionAuth for a few key reasons:
Complex configuration and learning curve: FusionAuth's extensive configuration options can make implementation challenging.
Infrastructure and maintenance overhead: Self-hosting FusionAuth requires teams to manage deployments, upgrades, monitoring, scaling, and security patches.
Limited visual workflow flexibility: Customizing authentication journeys, onboarding experiences, and MFA flows often requires additional code and configuration.
B2B multi-tenancy complexity: Supporting tenant-specific authentication policies, organizational hierarchies, and delegated administration can require additional development.
Enterprise SSO onboarding friction: Configuring SAML, OIDC, and SCIM across enterprise customers can introduce administrative overhead.
Pricing and feature restrictions: Advanced capabilities and commercial licensing can increase costs.
Each option below is a popular FusionAuth alternative, but they differ in strengths, deployment models, and how much infrastructure your team has to manage.
At a glance: FusionAuth alternatives compared
Alternative | Best for | Differentiator |
|---|---|---|
Descope | B2C and B2B SaaS teams that want managed auth with fast implementation and flexibility | Visual workflows, built-in multi-tenancy, self-service SSO and SCIM, and an MCP server for automating IAM |
Auth0 | Teams that want a mature, managed platform with broad ecosystem coverage | Large integration catalog and Actions for code-based extensibility |
Amazon Cognito | Teams already committed to AWS | Deep integration with API Gateway, IAM, and Lambda |
Firebase Authentication | Early-stage and mobile-first teams | Fastest setup and tight pairing with Firebase services |
Ory | Engineering-heavy teams that want API-first building blocks | Open-source foundation with a managed cloud option and Zanzibar-style permissions |
Microsoft Entra External ID | Organizations standardized on Microsoft and Azure | Conditional Access, Entra MFA, and a managed successor to Azure AD B2C |
Descope
Overview
Descope is a modern customer and agentic identity platform built for developers who want flexible, secure authentication without hosting, configuring, and maintaining their own identity infrastructure. As a fully managed platform, Descope handles deployments, upgrades, and security patching. This lets teams focus on the product instead of the identity server behind it.
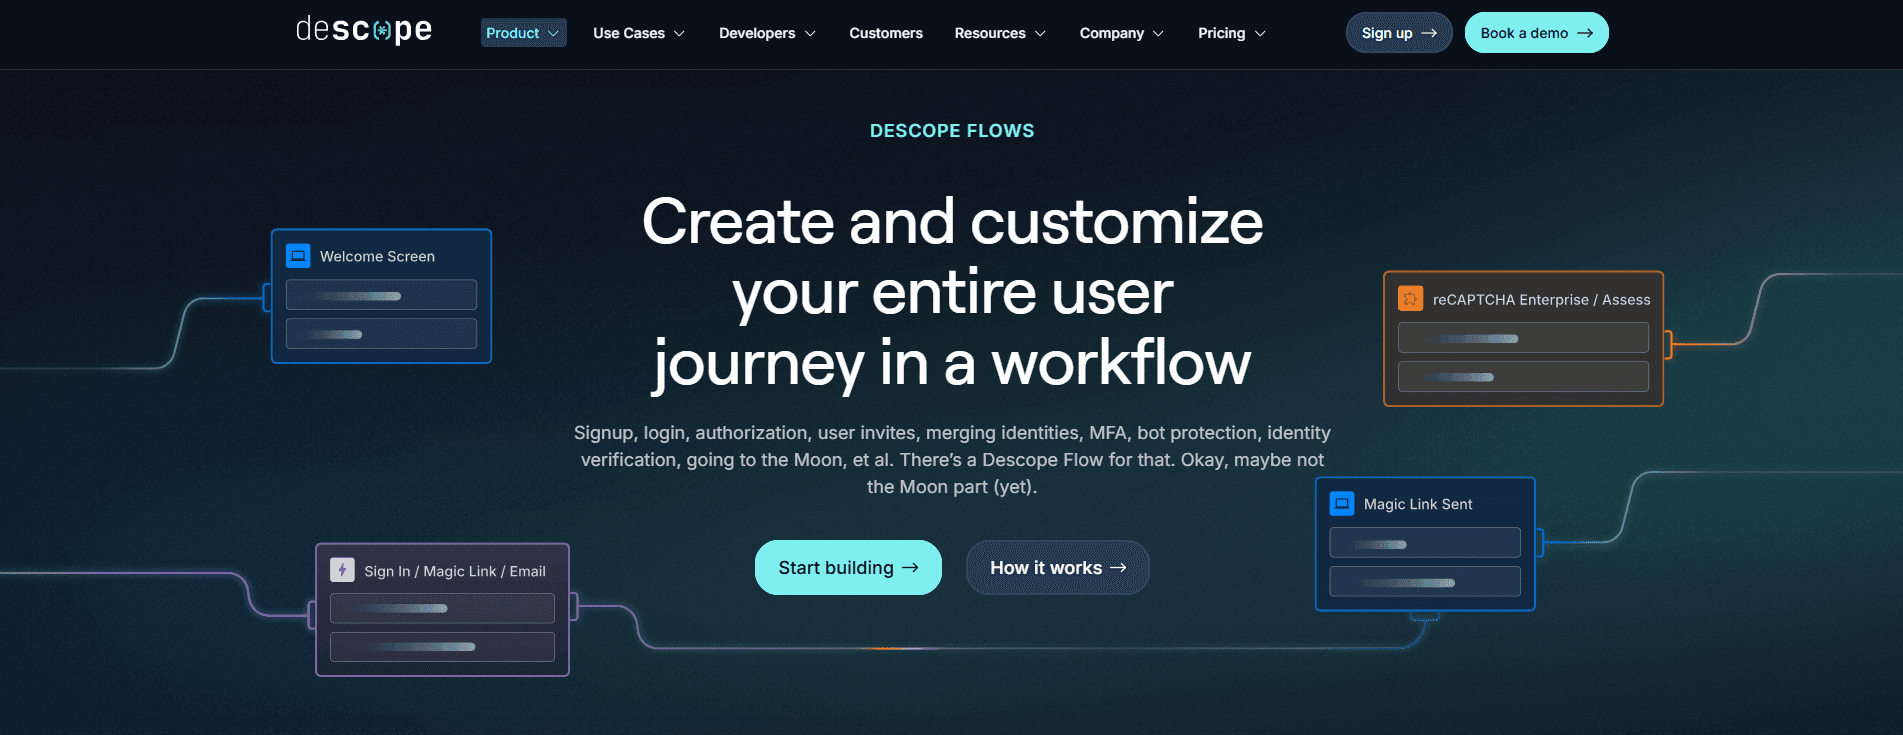
Descope is particularly well suited for B2B SaaS applications that require tenant-aware SSO, fine-grained authorization, and adaptable identity journeys. Its core differentiator is Flows, a no-code / low-code flow builder that allows teams to visually design and evolve authentication, MFA, SSO, consent, and agent authentication flows without redeploying application code.
Key capabilities
End-to-end identity orchestration across authentication, authorization, risk, and fraud in one platform.
Visual workflow editor for login, signup, MFA, SSO, and consent flows.
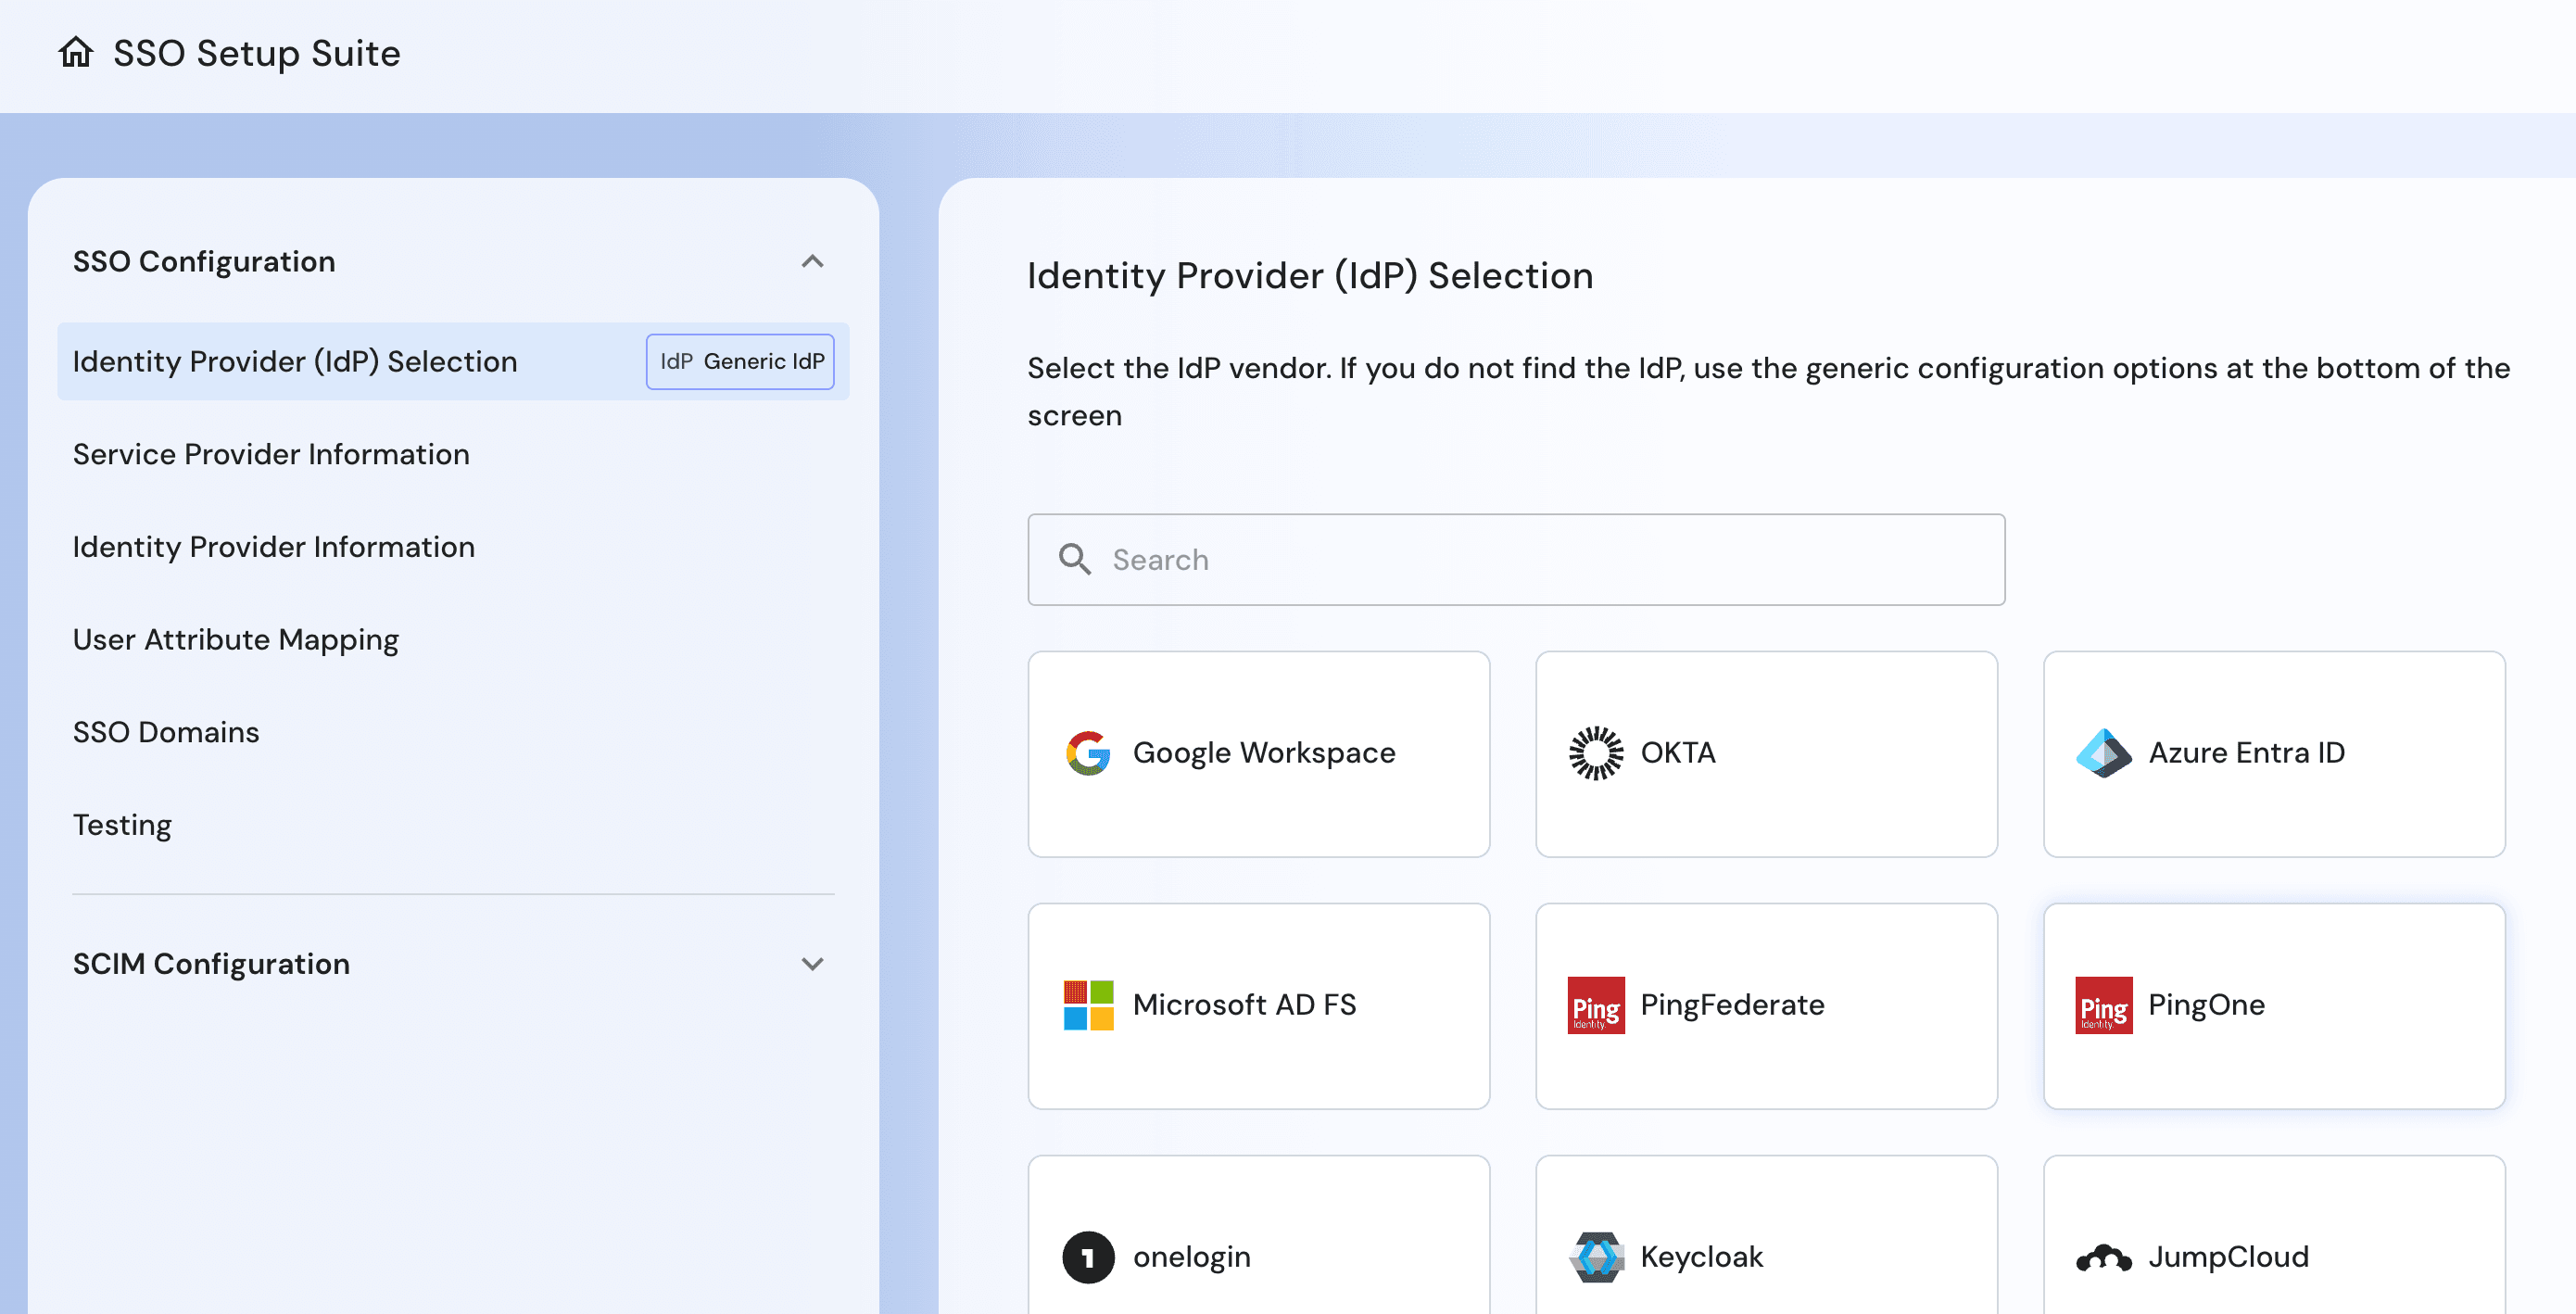
Enterprise SSO Setup Suite for guided SAML and SCIM onboarding and testing.
Adaptive MFA, session protection, and bot detection using native signals and third-party fraud integrations.
Plug-and-play connectors ecosystem with 50+ integrations for identity enrichment.
Support for passkeys, OTP, magic links, social login, and Google One Tap.
Embeddable user and admin UI components for self-service identity management.
15+ SDKs plus robust APIs for web, mobile, and backend integration.
Anonymous pre-auth user tracking for top-of-funnel visibility and conversion insights.
Agentic identity support for AI agents and MCP-based ecosystems.
Strengths
Fully managed, zero infrastructure: Descope eliminates the operational burden of self-hosting. There are no servers to provision, databases to maintain, upgrades to schedule, or security patches to apply.
Visual workflows instead of complex configuration: Descope lets developers design complete authentication, MFA, SSO, and authorization journeys in a drag & drop editor.
Unified multi-tenant identity: Descope natively supports tenant-aware users, roles, permissions, and authentication policies, along with delegated admin through embeddable widgets.
Streamlined enterprise SSO: Descope simplifies enterprise onboarding with guided SAML, OIDC, and SCIM setup, self-service configuration, and workflow-based SSO journeys. Admins can configure connections, certificates, and attribute mapping themselves.
Predictable pricing and responsive support: Descope offers transparent, usage-based pricing and consistently responsive support.
Passwordless by default: Descope supports passkeys, magic links, OTP, and social login as first-class methods that can be added to any flow without custom engineering.
Adaptive and risk-based MFA: MFA can be enforced dynamically using native signals and third-party risk integrations.
Developer-controlled UX: Descope supports both hosted components and fully custom UIs, giving developers control over branding and experiences.
Multi-region data residency: Descope enables EU-region data storage and processing, helping organizations comply with GDPR and regional data localization requirements.
FedRAMP Marketplace listing: Descope is FedRAMP High Authorized and listed on the FedRAMP Marketplace, supporting procurement by federal agencies and software companies in regulated industries that serve government organizations.
AI agent ready: Descope supports secure authentication and access control for AI agents and MCP servers with its Agentic Identity Hub.
Ideal for
Descope is a strong choice for developers and product teams that want the depth of a full-featured identity platform without the configuration complexity and infrastructure overhead that come with running FusionAuth.
Auth0
Overview
Auth0, now part of Okta, is one of the most widely adopted managed identity platforms. It provides hosted authentication, user management, and authorization for web, mobile, and API-driven applications. Auth0 offers a large integration catalog and an extensibility model built around Actions, which run custom code at key points in the login pipeline.
Key capabilities
Universal Login hosted pages with branding and customization options.
Social, enterprise, and passwordless connections including SAML and OIDC.
Actions for custom logic in login, registration, and token flows.
Marketplace of prebuilt integrations, extensions, and partner tools.
Strengths
Mature platform: Extensive documentation, quickstarts, and community resources make it easy to find answers for common implementation questions.
Broad protocol and connection support: Supports a wide range of social and enterprise identity providers, plus self-service SSO and SCIM for B2B.
Extensibility via Actions: Developers write Node.js code to customize the auth pipeline, such as enriching tokens or calling external APIs.
Ideal for
Teams that want a mature, managed platform with broad ecosystem coverage and are comfortable writing code to extend it. Evaluate costs carefully, as advanced features and higher MAU tiers can increase pricing significantly.
Amazon Cognito
Overview
Amazon Cognito is AWS's native authentication and user management service for web and mobile applications. It lets developers create user pools, handle sign-ups and logins, and manage permissions without hosting an identity server. Because it integrates tightly with other AWS services, Cognito is a natural choice for teams already operating in the AWS ecosystem.
Key capabilities
User pools for managing, storing, and authenticating application users.
Federated identity with SAML, OIDC, and social login providers.
Lambda triggers to customize authentication flows and user lifecycle events.
Built-in integration with API Gateway, AppSync, and other AWS services.
Strengths
Deep AWS integration: Works seamlessly with the broader AWS ecosystem, connecting authentication to services like API Gateway, IAM, and Lambda.
Managed scalability: As an AWS service, Cognito scales automatically without teams needing to provision or manage the underlying infrastructure.
Custom logic via Lambda triggers: Developers can insert custom behavior at different points in the authentication lifecycle using AWS Lambda functions.
Ideal for
Teams already committed to AWS and comfortable with its ecosystem. Less ideal for teams needing flexible UIs, native B2B multi-tenancy, or simpler configuration.
Firebase Authentication
Overview
Firebase Authentication is part of Google's Firebase platform, offering lightweight, fully managed authentication for mobile and web apps. Designed for fast setup, it suits small teams and early-stage products and integrates seamlessly with Firestore and Firebase Hosting. Teams needing enterprise features like SAML, OIDC, or multi-tenancy can upgrade to Google Cloud Identity Platform.
Key capabilities
Prebuilt UI components for login and signup flows.
Email/password, social, phone number, and anonymous user authentication.
SDKs for web, Android, iOS, and major frameworks.
Native integration with Firestore, Cloud Functions, and other Firebase services.
Strengths
Fast setup and simple integration: Developers enable common login methods in the console and integrate authentication quickly using client-side SDKs.
Mobile-first and cross-platform support: Firebase provides strong support for Android, iOS, and cross-platform frameworks like Flutter, Unity, and C++.
Seamless pairing with Firebase tools: Authentication works natively with Firestore, Realtime Database, and Firebase Hosting, ideal for teams already building on Firebase.
Ideal for
Mobile-first apps or early-stage teams that want a plug-and-play auth layer with minimal overhead. Less ideal for B2B SaaS teams that need tenant-level policies, delegated administration, or self-service enterprise SSO.
Ory Kratos
Overview
Ory is an identity platform built on open-source components covering authentication, OAuth2 and OpenID Connect, permissions, and access control. Teams can self-host the components or use Ory Network, Ory's managed cloud service, to avoid operating the stack. Its API-first, headless approach gives developers building blocks to assemble their own identity architecture.
Key capabilities
API driven identity and authentication primitives
Customizable login, registration, and account recovery flows
Self hosted or cloud managed deployment options
Integration with OAuth2 and authorization services through Ory components
Strengths
Open-source foundation with a managed option: Start with Ory Network for managed hosting while keeping the option to self-host, reducing long-term lock-in concerns.
Standards-based OAuth2 and OIDC: Hydra is a certified OpenID Connect provider, suiting teams acting as identity providers for APIs or partners.
Fine-grained authorization: Ory Keto brings Zanzibar-inspired, relationship-based permissions to applications that need more than basic role-based access control.
Ideal for
Ory Kratos is well suited for engineering teams that want flexible, API-first identity management without the overhead of self-hosting. Through Ory Network, teams can use Kratos as a managed service for authentication and user management while retaining control over identity flows and integrations. It appeals to developers seeking open-source flexibility, extensive customization, and managed infrastructure that reduces operational complexity.
Microsoft Entra External ID
Overview
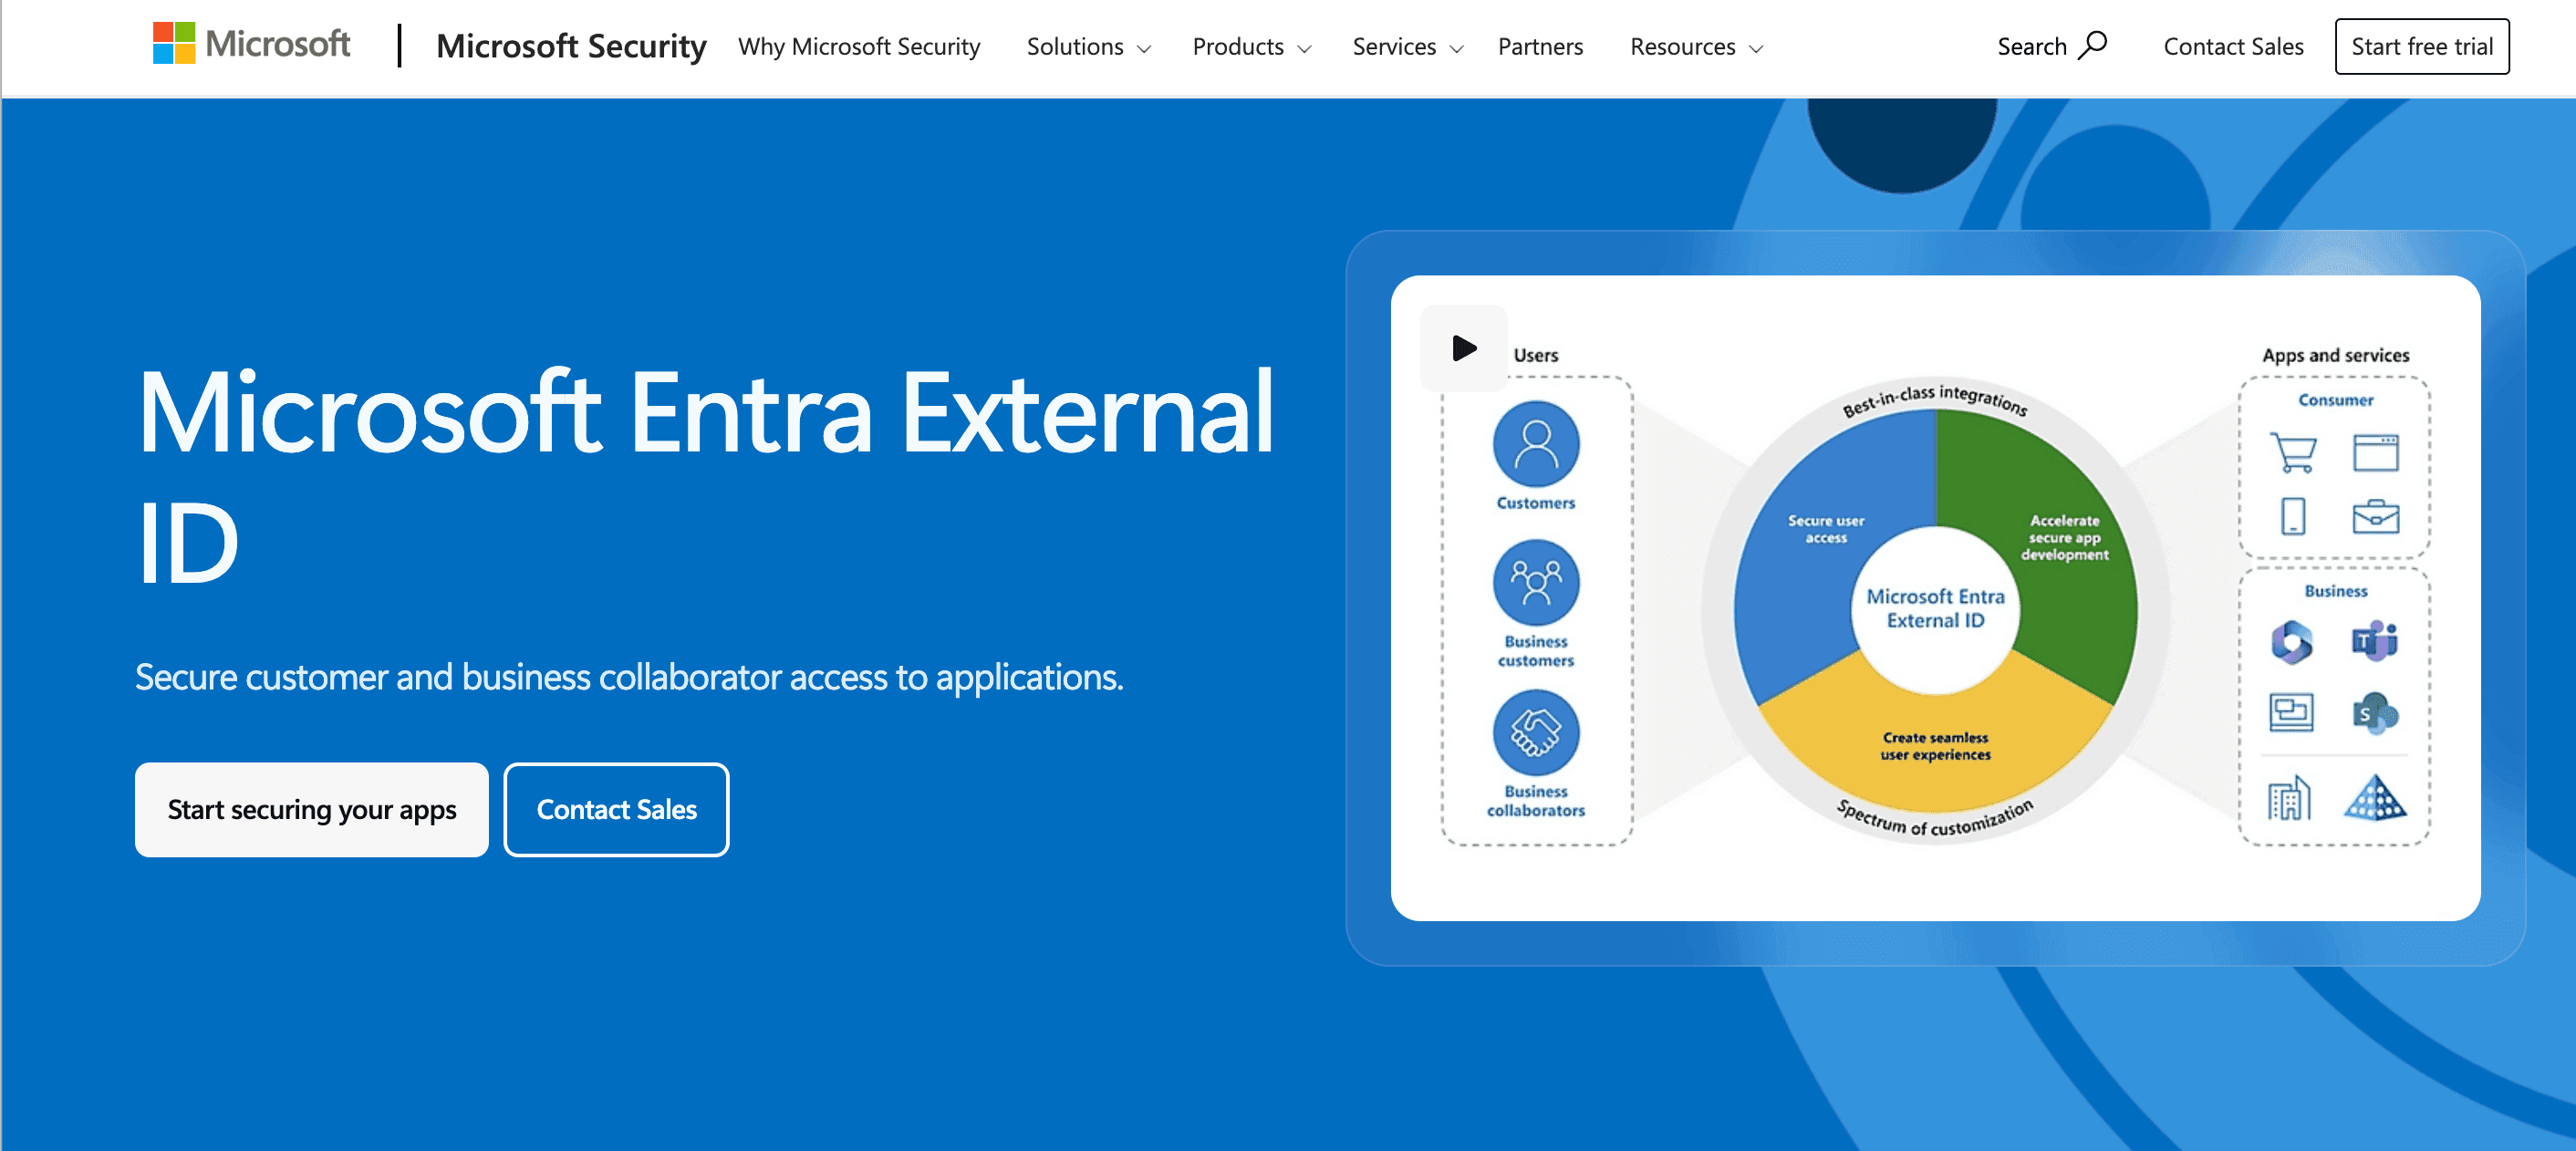
Microsoft Entra External ID is Microsoft's managed CIAM service and the successor to Azure AD B2C, which is no longer sold to new customers. It adds sign-up, sign-in, and profile management to customer-facing apps in a dedicated external tenant. Built on Microsoft Entra ID, it fits organizations already invested in Microsoft and Azure.
Key capabilities
Self-service registration and sign-in with social identities and enterprise identity providers
Customizable and branded user journeys for customer and partner-facing applications
Built-in security controls including conditional access, MFA, and risk-based policies
Identity lifecycle management with governance, access reviews, and expiration policies
Strengths
Deep Microsoft ecosystem integration: Works closely with Azure, Entra ID, and Microsoft security tooling, simplifying identity for teams on the Microsoft stack.
Enterprise-grade security controls: Conditional Access and Entra MFA bring Microsoft's proven security policy engine to customer-facing web and mobile apps.
Managed migration path from Azure AD B2C: Existing Azure AD B2C customers get a supported successor platform without running their own identity infrastructure.
Ideal for
Organizations standardized on Microsoft and Azure that want managed customer identity with enterprise security controls. Teams needing flexible, visual journey design or native B2B multi-tenancy for their own SaaS customers may require additional configuration and custom development.
Conclusion
Choosing the right FusionAuth alternative depends on your stack, scale, and goals. If your team wants to stop managing identity infrastructure and spend less time on configuration, a managed platform can significantly reduce operational overhead. Descope stands out for its visual workflows, native B2B multi-tenancy, self-service enterprise SSO, and support for B2C, B2B, partner, and agentic AI use cases, but each option above serves different developer needs.
For more detailed information on Descope, check out our docs. If you'd like a demo, meet with our auth experts. Also, if you want to try Descope yourself, sign up for a Free Forever Account and start dragging & dropping your auth today!