

Table of Contents
Don't have the time to read the entire post? Our human writers will be sad, but we understand. Summarize the post with your preferred LLM here instead.
Passwordless authentication is redefining how users access applications. By removing passwords, the weakest link in most security systems, it strengthens protection against phishing, credential stuffing, and account takeover while improving user experience. For developers and organizations alike, going passwordless is not just a security enhancement but a strategic shift toward simpler, safer digital experiences.
From consumer-facing apps to large-scale SaaS platforms, authentication plays a vital role in both trust and usability. A well-designed passwordless system can accelerate onboarding, reduce login friction, and lower support costs tied to password resets, all while maintaining compliance and scalability.
The top passwordless authentication solutions for 2026 include Descope, Auth0, Amazon Cognito, Microsoft Entra External ID, Firebase Authentication, OneLogin Customer Identity, Keycloak, Supabase, and HYPR, each suited to a different type of team and use case. Some are built for fast, no-code deployment, while others for deep ecosystem integration or full self-hosted control. The right pick depends on your developer experience needs, compliance requirements, and whether you also need to authenticate AI agents alongside human users.
In this guide, we compare the top 9 passwordless authentication solutions available today. Whether you’re evaluating a full identity platform or narrower passwordless authentication software focused on one piece of the login flow, we outline how passwordless authentication works, its key benefits, and which platforms best fit your business or technical requirements.
At a glance
The top passwordless authentication solutions for 2026 compared here are Descope, Auth0, Amazon Cognito, Microsoft Entra External ID, Firebase Authentication, OneLogin Customer Identity, Keycloak, Supabase, and HYPR.
Passwordless solutions replace passwords with methods such as passkeys, magic links, one-time passcodes, and biometrics, delivered through SDKs, APIs, or other abstraction layers.
Descope leads for teams that want to add and change passwordless flows through visual workflows, with passkeys, adaptive MFA, and AI agent authentication built in.
Auth0, Cognito, Entra External ID, and OneLogin suit ecosystem-aligned teams, while Firebase, Supabase, and Keycloak fit API-first and self-hosted use cases, and HYPR focuses on phishing-resistant workforce passwordless.
Choosing the right solution depends on your user scale, developer experience needs, pricing model, compliance requirements such as healthcare, and whether you also need to authenticate AI agents.
Quick facts
What passwordless authentication is | Sign-in methods that replace passwords with a possession or inherence factor, such as a passkey, magic link, or biometric scan |
What a passwordless solution provides | The SDKs, hosted flows, and admin tools needed to add and manage passwordless login without building the underlying protocols yourself |
Common methods | Passkeys and WebAuthn, magic links, one-time passcodes, biometric authentication, and social login |
How to choose | Weigh supported methods, developer experience, free tier availability, pricing model, and compliance needs against your team’s priorities |
Key outcome | Fewer credential-based breaches, faster onboarding, and lower support costs tied to password resets |
Common passwordless authentication methods
Passwordless authentication validates a user’s identity without requiring a password. Instead, it relies on secure factors such as passkeys, biometrics, one-time codes, or magic links that eliminate the risks of stolen, guessed, or reused credentials. For a full breakdown of how each method works, see What Is Passwordless Authentication and How It Works.
Modern passwordless systems combine several technologies to balance security and convenience:
Passkeys and FIDO2 / WebAuthn: Cryptographic credentials bound to devices that replace passwords with biometric or PIN-based authentication.
Magic links: Email-based one-click sign-ins that skip password entry entirely.
One-time passcodes (OTPs): Temporary verification codes sent via email, SMS, or app notification.
Biometric authentication: Fingerprint, facial recognition, or hardware token verification tied to the user’s device.
OAuth and social logins: Users sign in with existing Google, Apple, or LinkedIn accounts via OAuth 2.0, reducing friction and boosting conversion.
Unlike traditional password-based systems, passwordless authentication removes the most common vector for breaches and user frustration. It delivers a frictionless sign-in flow that is more secure, faster to deploy, and easier for end users to adopt.
The right passwordless platform helps organizations reduce login friction, defend against phishing, meet compliance mandates, and scale across multiple applications or tenants. Below, we compare today’s leading passwordless authentication solutions, highlighting their capabilities, strengths, and ideal use cases.
Also read: 4 Benefits of Passwordless Authentication
Comparing the top passwordless authentication solutions
Here is how the nine solutions stack up side by side before the deep dives below.
Provider | Best for | Passwordless methods | Developer experience | Pricing model |
|---|---|---|---|---|
Descope | Teams wanting to avoid custom auth code | Passkeys, magic links, OTP, biometrics, social login | Visual workflow editor, 15+ SDKs, prebuilt UI widgets | Usage-based |
Auth0 | Enterprise-grade protocol coverage | Passkeys, WebAuthn, magic links, OTP | Hosted pages, Actions, Hooks, large SDK ecosystem | Tiered, usage-based |
Amazon Cognito | Teams already built on AWS | FIDO2 and WebAuthn passkeys, OTP | Lambda triggers, deep AWS service integration | Usage-based |
Microsoft Entra External ID | Microsoft-native enterprises | FIDO2 keys, Windows Hello, Microsoft Authenticator | Conditional Access policies, Microsoft 365/Azure integration | Per-user, tiered |
Firebase Authentication | Mobile-first startups | Email link sign-in, OTP, Google One Tap | Prebuilt UI libraries, fast setup | Usage-based |
OneLogin Customer Identity | Mixed cloud and on-prem enterprises | Biometric verification, OTP, push notifications | Centralized SSO, directory sync | Quoted |
Keycloak | Self-hosted, full control | FIDO2 and WebAuthn | Fully customizable, open-source | Self-hosted, no license cost |
Supabase | Developers wanting backend plus auth | Magic links, OTP, social login | Postgres-based, edge functions | Usage-based |
HYPR | Phishing-resistant workforce passwordless | FIDO2-certified cryptographic credentials | Decentralized architecture, IAM integrations | Quoted |
Descope
Best for: Developers and product teams that want to add and adapt passwordless authentication through abstraction layers (visual workflows, SDKs, MCP server) instead of building it from scratch, including teams that also need to authenticate AI agents.
Overview
Descope is a modern identity platform built to make passwordless authentication simple, secure, and adaptable for any external-facing application. Designed for developers and product teams, Descope replaces traditional password-based systems with frictionless login experiences such as passkeys, magic links, one-time passcodes, and social login. Its visual workflow editor and extensive SDK library allow teams to design and deploy custom authentication flows without complex backend code or infrastructure management.
Beyond passwordless login, Descope supports multi-tenant SSO, adaptive MFA, and fine-grained access control across B2C and B2B environments. It provides built-in orchestration tools that let developers connect risk engines, fraud tools, and external identity providers within a single, unified flow. This approach makes it possible to deliver seamless, secure access across all user types, including end customers, business partners, and even AI agents and MCP servers.
Key capabilities
Comprehensive passwordless authentication: Support for passkeys, OTP, magic links,social login, and Google One Tap, giving users multiple secure, frictionless ways to sign in without passwords.
Visual workflow editor: Drag and drop passwordless and MFA flows to design custom login experiences without writing backend code.
Adaptive MFA and security controls: Protect accounts with context-aware MFA, session management, and bot detection that respond dynamically to risk.
Backup auth methods: Add conditional steps to provide backup auth and MFA methods when primary methods fail (e.g. when the end user’s device is not WebAuthn-compatible).
Prebuilt UI widgets: Quickly embed self-service passwordless auth (e.g. adding passkeys and authenticator apps) and account recovery components (e.g. resetting passwords) into any web or mobile app.
SDKs and APIs for modern frameworks: Broad developer coverage across 15+ SDKs, including Next.js, Flutter, React Native, and more.
AI agent and MCP server authentication: Issue scoped, short-lived credentials for AI agents through the Agentic Identity Hub, alongside standard human user authentication.
Connector ecosystem: Integrate seamlessly with third-party tools for risk, fraud, analytics, and directory sync.
Integration-ready orchestration: Enrich user journeys with data and actions from third-party fraud, go-to-market, and compliance tools.
Strengths
End-to-end passwordless experience: Built-in support for passkeys, magic links, OTP, biometrics, and social login enables fully passwordless authentication across web and mobile.
Faster implementation: Visual workflows let teams design and test passwordless flows without backend complexity or infrastructure setup.
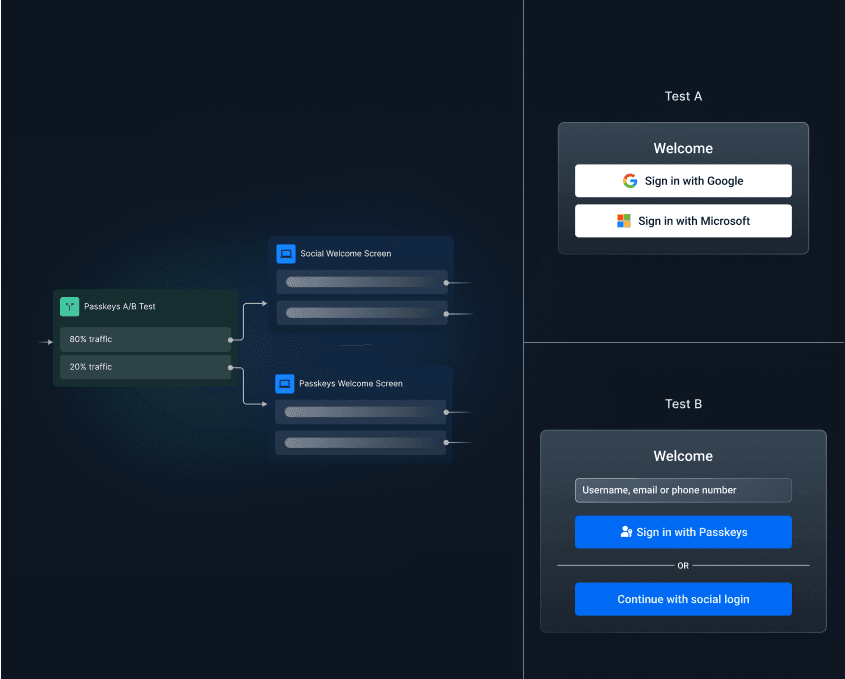
Experimentation-friendly: Create A/B tests to randomize traffic between different onboarding paths and auth methods for data-driven and phased rollouts.
Adaptive security: Risk signals trigger additional MFA only when needed, balancing protection with a seamless user experience.
Developer-first design: SDKs, APIs, and embeddable components make it easy to integrate passwordless authentication into any stack.
Scalable for every use case: From consumer apps to multi-tenant SaaS platforms, Descope supports passwordless login for every audience, including AI agent traffic.
Transparent pricing and support: Predictable usage-based pricing and responsive developer assistance for teams of any size.
Limitations
As a newer platform than legacy identity providers, Descope has a smaller enterprise case study library than incumbents that have been in market for over a decade, though its production customer base–including Databricks, Collectors, and GoodRx—is growing quickly. Teams with heavy investment in a specific cloud ecosystem’s native tooling may also find less pre-built infrastructure glue than a same-vendor option like Cognito or Entra External ID.
Ideal for
Descope is ideal for developers and product teams building consumer or SaaS applications that need passwordless authentication, multi-tenant SSO, and adaptive MFA without the complexity of managing identity infrastructure. It’s equally suited for startups launching fast and enterprises modernizing legacy systems. With Descope, teams can deploy secure, user-friendly login experiences that scale with their products, customers, and AI agents.
Auth0
Best for: Organizations that need enterprise-grade passwordless authentication with broad protocol support and are prepared for the added complexity and tiered pricing.
Overview
Auth0, part of Okta, is one of the most widely recognized identity platforms offering hosted authentication for web, mobile, and enterprise applications. It provides support for passwordless authentication methods such as WebAuthn passkeys, magic links, and one-time passcodes, along with adaptive MFA and enterprise SSO.
Auth0’s extensibility through Actions, Hooks, and APIs makes it flexible for custom logic and advanced integrations, though setup and maintenance can become complex as projects scale.
Key capabilities
Support for passkeys, WebAuthn, magic links, and one-time passcodes
Hosted login pages with customization and branding options
Adaptive MFA for step-up verification based on risk and context
SSO and federation using SAML, OIDC, and social identity providers
Actions and Hooks for custom logic within the authentication pipeline
Strengths
Passwordless support: Built-in passkey and WebAuthn options deliver phishing-resistant login experiences.
Enterprise readiness: Supports SSO, directory sync, and advanced access policies for large organizations.
Developer ecosystem: Documentation, SDK coverage, and a large integration marketplace.
Limitations
Pricing can escalate at scale, particularly once add-ons for advanced MFA, enterprise connections, or higher MAU tiers are factored in. Building fully custom passwordless flows can require more configuration through Actions and Hooks than a visual, no-code workflow.
Ideal for
Organizations that need enterprise-grade passwordless authentication with broad protocol support and are prepared for the added complexity and tiered pricing.
Amazon Cognito
Best for: Teams already invested in AWS that want to keep passwordless authentication close to their existing infrastructure.
Overview
Amazon Cognito is AWS’s managed authentication and user management service that provides passwordless and password-based login options for web and mobile applications. It supports FIDO2 and WebAuthn passkeys, one-time passcodes, and integration with major social and enterprise identity providers. Cognito is tightly integrated with the broader AWS ecosystem, making it a natural choice for developers already building on AWS infrastructure.
However, configuration complexity and limited no-code capabilities can make it difficult to scale or customize user experiences.
Key capabilities
Passwordless authentication using FIDO2 and WebAuthn passkeys
One-time passcode (OTP) login and multi-factor authentication support
Identity federation with SAML, OIDC, and social providers
Deep integration with AWS services like API Gateway, AppSync, and IAM
Customizable authentication logic using AWS Lambda triggers
Strengths
AWS ecosystem alignment: Works with other AWS tools and services.
Passwordless options: Native FIDO2 and WebAuthn support enhance login security.
Custom logic through Lambda: Developers can extend and modify authentication flows with serverless functions.
Limitations
UI customization is limited compared to platforms built around visual editors, multi-tenant identity for B2B apps typically needs custom workarounds, and there is no visual, drag-and-drop workflow tooling for building or adjusting login flows.
Ideal for
Teams already invested in AWS that want to leverage native passwordless capabilities while keeping authentication close to their infrastructure.
For organizations that need more flexibility or visual orchestration, Descope enhances AWS-native auth with an AWS SaaS Builder Toolkit plugin to add passkeys, adaptive MFA, and drag-and-drop passwordless flows. It can also extend Cognito as an OIDC Provider.
Microsoft Entra External ID
Best for: Large organizations and regulated industries that need enterprise passwordless authentication integrated with compliance, governance, and access control.
Overview
Microsoft Entra External ID enables organizations to manage both workforce and external identities with strong support for passwordless authentication. Through FIDO2 security keys, Windows Hello for Business, and Microsoft Authenticator app sign-ins, Entra External ID helps enterprises reduce password-related risks while maintaining compliance and governance.
It integrates tightly with Microsoft 365, Azure, and thousands of SaaS applications, making it a common choice for organizations already operating within the Microsoft ecosystem.
Key capabilities
Passwordless login using FIDO2 security keys, Windows Hello, and Microsoft Authenticator
Adaptive access policies that evaluate user, device, and session risk
Lifecycle management with access reviews, provisioning, and audit logging
Conditional Access policies for contextual and risk-based authentication
Strengths
Enterprise-grade passwordless authentication: Native FIDO2 and Windows Hello support deliver secure login experiences.
Comprehensive governance: Built-in tools for audit trails, compliance, and lifecycle management.
Adaptive security: Policies dynamically adjust access based on user behavior and device posture.
Limitations
Entra External ID is tightly coupled to the Microsoft ecosystem and less flexible for multi-cloud teams that need to integrate with a broader mix of identity providers. The External ID feature set is still maturing relative to Microsoft’s longer-established workforce Entra ID product.
Ideal for
Large organizations and regulated industries that need enterprise passwordless authentication integrated with compliance, governance, and access control.
Firebase Authentication
Best for: Startups, small teams, and mobile developers looking for simple passwordless authentication that can be launched quickly.
Overview
Firebase Authentication is Google’s developer-focused identity service that simplifies user sign-in for web and mobile apps. It supports passwordless authentication methods such as email link sign-in, one-time passcodes, and Google One Tap.
Built directly into the Firebase platform, it integrates with other Google services like Firestore, Cloud Functions, and Firebase Hosting. While ideal for small teams and mobile-first products, Firebase can become difficult to scale or migrate from as applications grow.
Key capabilities
Passwordless authentication via email link sign-in, OTP, and Google One Tap
Support for social login with Google, Apple, and Facebook
Anonymous sign-in for guest user sessions
Prebuilt UI libraries for web, iOS, and Android applications
Integration with other Firebase services such as Firestore and Cloud Functions
Strengths
Fast setup: Developers can enable passwordless and social login methods.
Mobile-first experience: Optimized for Android, iOS, and cross-platform development.
Seamless ecosystem: Works natively with Firebase and Google Cloud services.
Limitations
Enterprise federation and multi-tenant management are limited compared to a dedicated customer identity platform. Passwordless options are narrower in scope, lacking native passkey and adaptive MFA depth found in CIAM-focused competitors.
Ideal for
Startups, small teams, and mobile developers looking for simple passwordless authentication that can be launched quickly. Firebase Auth is ideal for projects already using Google Cloud or Firebase, though larger teams may encounter challenges with customization and vendor lock-in as their needs evolve.
Also read: Add Passkeys to Firebase / GCP Identity Using Descope
OneLogin Customer Identity
Best for: Mid-market and enterprise organizations that want to adopt passwordless and adaptive authentication without rebuilding their existing infrastructure.
Overview
OneLogin is an enterprise identity solution that supports both traditional and passwordless authentication methods for employees, customers, and partners. It offers secure access through one-time passcodes, biometric verification, and adaptive MFA, helping organizations reduce reliance on passwords while maintaining strong access controls.
Key capabilities
Passwordless login through biometric verification, OTP, and push notifications
Adaptive MFA with contextual risk analysis and policy enforcement
Centralized SSO across cloud and on-prem applications
Directory sync and automated provisioning for external users
Strengths
Passwordless options: Supports multiple passwordless methods, including biometrics and one-time codes.
Adaptive protection: Analyzes risk signals to determine when additional verification is needed.
Security-focused design: Built to reduce credential theft and unauthorized access.
Limitations
OneLogin is more workforce and enterprise-oriented in its design center, and it is less developer-first than platforms built around SDKs, APIs, and visual workflow builders for customer-facing apps.
Ideal for
Mid-market and enterprise organizations that want to adopt passwordless and adaptive authentication without rebuilding their existing infrastructure. OneLogin is well-suited for teams prioritizing access across mixed cloud and on-prem environments.
Keycloak
Best for: Organizations with strong DevOps resources that want to self-host passwordless authentication and maintain complete control over configuration and data.
Overview
Keycloak is an open-source identity and access management solution originally developed by Red Hat that gives organizations full control over their authentication stack. It supports passwordless authentication through FIDO2 and WebAuthn, allowing users to sign in securely with device-bound credentials or biometrics instead of passwords.
Because it is self-hosted, Keycloak offers maximum flexibility and customization, though it also introduces operational overhead, upgrade challenges, and scaling complexity as deployments grow.
Key capabilities
Passwordless authentication using FIDO2 and WebAuthn
Support for OIDC, SAML, and LDAP for broad interoperability
Customizable login pages and authentication flows
Built-in admin console for managing users, roles, and realms
Strengths
Full customization: Control every aspect of passwordless authentication and authorization.
Open-source flexibility: No licensing costs and freedom to modify source code.
Protocol coverage: Supports enterprise standards such as SAML, OIDC, and LDAP.
Limitations
Keycloak is self-hosted, so it requires dedicated DevOps resources for deployment, upgrades, and scaling, and there is no managed cloud option from the project maintainers, meaning your team owns uptime and security patching directly.
Ideal for
Organizations with strong DevOps resources that want to self-host passwordless authentication and maintain complete control over configuration and data. Keycloak is best suited for enterprises or government environments that prioritize flexibility and compliance but can manage the added complexity of updates, scaling, and maintenance.
Supabase
Best for: Developers and startups looking for open-source passwordless authentication with direct database integration.
Overview
Supabase Auth is the authentication service built into the open-source Supabase platform. It provides developers with lightweight, passwordless authentication options such as magic links, one-time passcodes, and social login, all backed by a secure Postgres database.
Supabase offers a Firebase-like developer experience with open-source transparency and flexible deployment options, making it an appealing choice for startups and teams that want more control over their data.
Key capabilities
Passwordless authentication via magic links and one-time passcodes (OTP)
Support for social login providers such as Google, GitHub, and Apple
Postgres-based user management with row-level security for granular access control
Serverless edge functions for extending authentication logic
Strengths
Open-source flexibility: Full transparency and the ability to self-host without vendor lock-in.
Built-in passwordless methods: Magic links and OTPs make login simple for users and easy to implement.
Postgres integration: Tight coupling with Postgres allows fine-grained authorization and data control.
Limitations
Authentication is one part of a broader backend platform rather than the core product, so advanced passwordless and enterprise identity features—such as adaptive MFA or multi-tenant SSO—are less deep than what a dedicated identity provider offers.
Ideal for
Developers and startups looking for open-source passwordless authentication with direct database integration. For teams seeking advanced features such as multi-tenant SSO, adaptive MFA, or FIDO2 passkey support, Descope can integrate directly with Supabase to expand authentication capabilities without re-platforming.
Also read: Add Passkeys to Supabase With Descope
HYPR
Best for: Enterprises and regulated industries that require phishing-resistant passwordless authentication with full compliance and strong assurance.
Overview
HYPR is an enterprise-grade passwordless authentication platform focused on eliminating shared secrets and preventing credential-based attacks. Its HYPR Authenticate solution replaces passwords with FIDO2-certified, phishing-resistant authentication powered by public-key cryptography.
HYPR’s decentralized architecture stores private keys on the user’s device rather than in a centralized server, minimizing the attack surface and reducing the risk of credential theft. It is built for large organizations that need high assurance, regulatory compliance, and seamless user experiences across workforce, customer, and partner access.
Key capabilities
Passwordless authentication using FIDO2-certified cryptographic credentials
HYPR Authenticate app for secure biometric or PIN-based login across devices
Decentralized identity model that keeps private keys on user devices
Multi-factor authentication (MFA) without passwords or shared secrets
Strengths
Phishing-resistant authentication: Private keys never leave the device, protecting against replay and credential attacks.
Decentralized security: Eliminates password databases and reduces breach risk.
Enterprise integrations: Works with major IAM platforms and SSO providers.
Limitations
HYPR is focused on phishing-resistant workforce passwordless, so it is a narrower fit for consumer-facing customer identity than a full CIAM platform. Its pricing is quote-based rather than self-service.
Ideal for
Enterprises and regulated industries that require phishing-resistant passwordless authentication with full compliance and strong assurance. HYPR is best suited for organizations prioritizing security, scalability, and risk reduction over rapid developer customization.
How to choose the right passwordless authentication solution
The right passwordless authentication solution depends less on which vendor is “best” overall and more on which priority matters most for your team right now.
If your priority is | Consider | Why |
|---|---|---|
Developer abstraction layers + AI agent auth | Descope | Visual workflows and an Agentic Identity Hub cover both human and AI agent authentication without custom protocol work |
Ecosystem extensibility | Auth0 or Descope | Integration / connector ecosystems and SDKs support deep custom logic |
AWS-native infrastructure | Amazon Cognito | Deep integration with API Gateway, AppSync, IAM, and Lambda keeps auth close to existing AWS workloads |
Microsoft-native infrastructure | Microsoft Entra External ID | Tight integration with Microsoft 365, Azure, and Conditional Access policies |
Mobile-first apps | Firebase Authentication or Descope | Firebase: Prebuilt UI libraries and fast setup optimized for Android and iOS; Descope: Native mobile auth SDKs that enable passwordless auth without redirects |
Backend plus auth in one platform | Supabase | Postgres-based user management with row-level security alongside authentication |
Full control, self-hosted | Keycloak | Open-source with no licensing costs and complete configuration control |
Phishing-resistant workforce passwordless | HYPR | Decentralized, FIDO2-certified architecture built for high-assurance enterprise environments |
Go passwordless with Descope
Descope lets teams add and adapt passwordless authentication—including passkeys, magic links, OTPs, and adaptive MFA—through visual workflows and SDKs instead of building it from scratch. Teams can extend the same identity layer to authenticate AI agents and MCP servers as user-facing traffic grows more automated. For a deeper look at how Descope simplifies passwordless authentication, check out our docs.
Sign up for a Free Forever account to get started, or book a demo with our experts if you have questions first.