Table of Contents
Don't have the time to read the entire post? Our human writers will be sad, but we understand. Summarize the post with your preferred LLM here instead.
Every app with more than one kind of user has to decide who can do what: which records a user can read, which settings an admin can change, and which actions a service can take. That decision is authorization. It runs after authentication, which confirms who a user is, and it applies to people, devices, and software. Authorization mistakes are among the most common security flaws in web applications, whether the app belongs to a startup or an enterprise.
At a glance
Authorization decides what an authenticated user, device, or service can do and which resources it can reach.
Authentication confirms who you are, while authorization decides what you can access once you’re in.
In identity and access management (IAM), authorization is set through roles, attributes, or relationships, as in role-based (RBAC), attribute-based (ABAC), and relationship-based (ReBAC) access control.
After login, roles and permissions often travel with the user’s session token, such as a JSON Web Token (JWT), and the app checks them before allowing an action.
What is authorization?
Authorization in cybersecurity refers to the process of granting or denying access to resources based on the identity and permission level of a user or device (collectively referred to as an entity). In identity and access management (IAM), authentication proves who someone is, while authorization controls what they can do.
The authorization process implements access controls that determine the exact activities an entity is allowed to perform on a specific resource. Authorization may be granted to entities on a case-by-case basis or according to a predetermined model, such as role-based access control, covered below.
Authorization is a core part of cybersecurity, protecting the confidentiality, integrity, and availability of data and resources within an IT environment. It ensures that only authorized users can access those resources and act on them, whether the threat is an internal mistake or an external attack. Properly set authorization also contains the damage when something goes wrong by limiting each entity to the least amount of data it needs to do its job.
For example, Jane is an employee at XYZ Corporation. She logs in to the company’s document management system. Once logged in, Jane has access to edit and create documents in the Sales folder because she is part of the sales team. However, she cannot access the HR folder as she doesn’t have the necessary permissions.
Authorization vs. authentication
Authorization works in tandem with authentication. Before a user is granted access, they must first confirm their identity through an authentication method, such as a username and password, social login, or biometrics.
Voting in an election illustrates the distinction:
Checking in at the polling station, where poll workers confirm a voter’s identity against the voter rolls, authenticates the individual.
The voter’s registration then determines what they’re authorized to do. Depending on criteria such as political party affiliation or location, some voters may hold additional authorizations, such as voting in a party’s primary or voting by mail.
Authentication | Authorization | |
|---|---|---|
Definition | Verifying the identity of a user, system, or process. | Granting or denying access to resources based on the authenticated user's permissions. |
Purpose | Confirming the user is who they claim to be. | Determining what actions or resources a user is allowed to access. |
Focus | Identity verification. | Access control. |
Process | Usually involves verifying credentials (e.g., username/password, biometrics). | Involves checking if the authenticated user has the necessary permissions for the requested action/resource. |
Goal | Ensuring only authorized users gain access. | Restricting access to specific functionalities or data based on permissions. |
Examples | Logging into an email account with a username and password. | A user with 'admin' privileges being able to configure system settings. |
Learn more: Authentication vs Authorization
How does authorization work?
Authorization grants or denies access based on the user’s permission level. For example, an employee may have read-only access to specific files, while a manager may have read-write access.
An access control system typically manages authorization, enforcing the organization’s policies and rules through the following steps:
Initial authentication: First, users must confirm their identities, typically by entering a username and password or using a passwordless method.
Authorization request: Once the user is authenticated, they can request access to a particular resource. This request includes user details, such as a username, and relevant attributes, such as role or group affiliation.
Access control evaluation: The access control system receives the authorization request and checks whether the user can access the requested resource. This typically involves checking policies or rules defining who can access resources under what conditions.
Authorization decision: Based on the access control policies, the system makes a decision, either granting or denying the user’s request. If the user is granted permission, they can access the resource. If access is denied, the user is informed that they do not have permission to access the resource.
Activity logging: Following the authorization decision, the system records all relevant information, such as the time of access, the user’s identity, and activity. This information can be used for auditing and compliance purposes and for detecting and investigating security incidents.
Revoking permissions: Access permissions can be withdrawn at any time, either automatically (based on predefined policies) or manually (by an administrator). When access is revoked, the user can no longer access the resource. The revocation is logged for auditing and investigation.
B2B Enterprise Readiness Checklist
Score your tech stack on enterprise readiness pillars - from dev and IT experience to security and architecture.
Download
How apps check authorization after login
After a user logs in, the app receives a session token, often a JWT. The token can carry the user’s roles and permissions as claims, so the app’s backend can validate it and check those claims on each request without a separate lookup. For example, Descope includes a user’s roles and permissions at both the project and tenant levels in the session JWT.
Claims work well for broad checks, like whether a user is an admin. They’re a poor fit for fine-grained checks, such as whether a user owns a specific document, because a token can’t list every resource a user can reach, and its claims stay fixed until the token is refreshed. For those checks, the app queries an authorization service at request time.
Types of authorization
Most authorization is granted through one of three main access control models:
Role-based
Relationship-based
Attribute-based
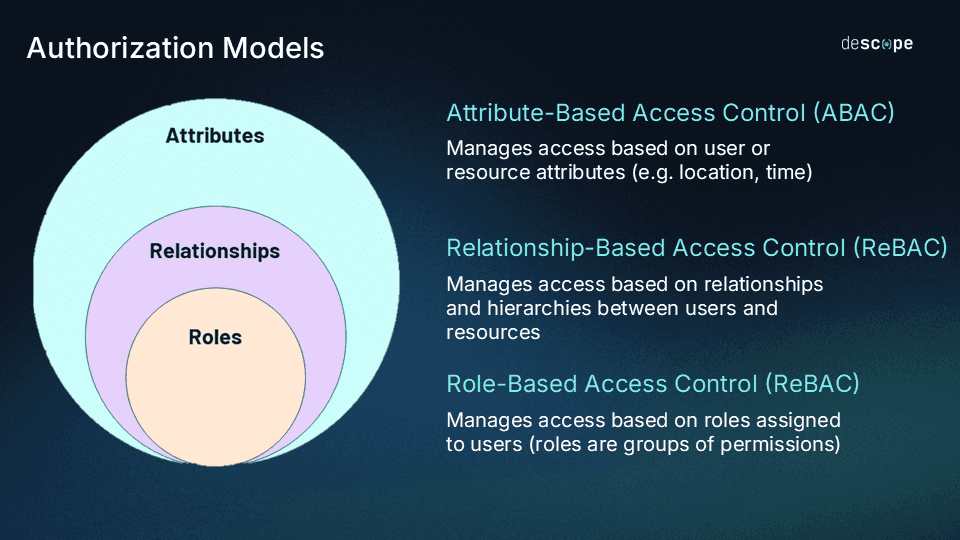
Attribute-based models are the broadest way to grant authorization since anything can theoretically be considered an attribute. Roles can be viewed as a subset of attributes, and relationships fall somewhere in between.
Role-Based Access Control (RBAC)
RBAC is a method of authorization that assigns users to specific roles based on their job responsibilities. Each role has a set of permissions that determine what actions the user can perform.
For example, a bookkeeper in an accounting department may have read-only access to financial reports, while a senior accountant may have read-write access.
Attribute-Based Access Control (ABAC)
ABAC determines user authorizations by the attributes associated with their identity or account. These attributes may include their job title (as with RBAC) but also other factors such as location, department, team lead, shift, current projects, etc.
As a result, ABAC is more granular than RBAC, allowing for more precise control over user access.
Learn more: RBAC vs. ABAC: What’s the Difference?
Relationship-Based Access Control (ReBAC)
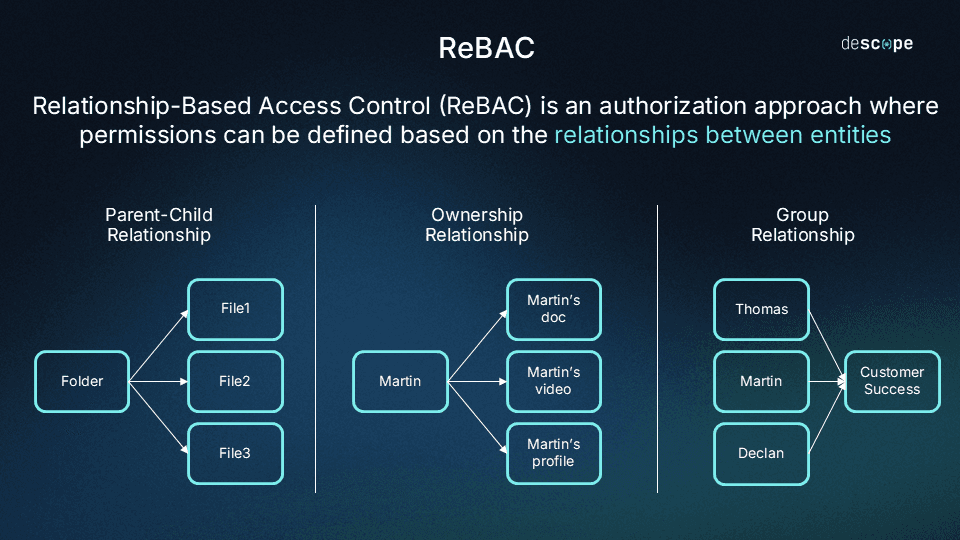
ReBAC determines authorization based on relationships between resources and identities (or users). Some of these relationships include:
Data ownership: For example, after you create a post on LinkedIn, you can edit and delete it. However, you can’t edit or delete the posts of others. You have these permissions for the posts you create since you are the “owner” of these posts.
Parent-child relationships: For example, if you have “edit” permissions for a folder, you automatically have “edit” permissions on all the files within that folder, since the folder and files have a parent-child hierarchy.
User groups: Rather than individually assigning permissions to roles, you can place users in groups and assign permissions to the whole group. This approach avoids ballooning roles with individual permissions as organizations grow in size.
Learn more: RBAC vs ReBAC: Which Is Right for You?
Other access control models
Two older access control models:
Mandatory Access Control (MAC): a central authority assigns security labels to data based on its sensitivity, and users can access only the data their clearance allows. Users can’t change these rules.
Discretionary Access Control (DAC): the opposite of MAC, DAC leaves authorization decisions to individual discretion. The resource owner most commonly has the deciding vote.
Real-world examples of authorization in software
Authorization models deploy in countless configurations across diverse scenarios, from consumer-facing apps to B2B platforms.
Authorization in operating systems: Operating systems often restrict access to sensitive files and settings. For example, a user may be required to enter an administrator password to install software or modify system settings.
Authorization in web applications: Web applications use authorization to restrict access to certain pages or features. For example, a user may need to be logged in and have a certain level of permission to view customer data or place an order.
Authorization in databases: Databases use authorization to restrict access to sensitive data. For example, a user may only be able to view data from a specific table or have read-only access to certain fields.
Authorization in cloud environments: Cloud environments use authorization to restrict access to virtual machines (VM), storage, and other resources. For instance, a user may be assigned the “VM Operator” role, which allows them to start, stop, and restart VMs. Another user may be assigned the “VM Administrator” role, which grants them complete control over the VMs.
Authorization in Internet of Things (IoT) devices: Authorization is a critical mechanism used to secure and control access to sensitive settings or data on connected devices. For example, the owner of a smart home security camera may be able to change its settings and share access, while other household members can only view the live feed.
Authorization in B2B SaaS apps: A user can be an admin in one customer’s tenant and a regular member in another. These roles are scoped per tenant, which is RBAC, so the same person gets different permissions depending on the tenant they’re working in.
Authorization in document apps: The person who creates a file can delete it, while collaborators can only edit it. Access follows the relationship between each user and the document, which is ReBAC.
Authorization in feature and region gating: An app can open a feature only for a certain subscription tier, or block a request from a country it doesn’t serve. The decision depends on attributes of the user or request, which is ABAC.
Common authorization challenges
Broken access control holds the #1 position in the OWASP Top 10:2025, and OWASP reports that 100% of the applications tested were found to have some form of it. Common challenges include the following:
Lack of understanding: Authorization depends on complex models that require active management. Organizations that don’t understand these models can end up with misconfigurations, security vulnerabilities, and authorizations that were improperly granted or never revoked (i.e., “permission bloat”).
Weak authentication: Weak passwords and inadequate authentication methods can make it easy for attackers to take over legitimate accounts, inherit their authorizations, and further infiltrate the environment.
Insufficient monitoring: Organizations are always changing, as users join, change roles, and leave. Over time, keeping track of who has which authorizations gets harder, and without the right monitoring, organizations will struggle to detect unauthorized access or changes to authorization settings.
Human error: People are responsible for security configurations and, in some cases, data entry. Their mistakes can cause misconfigurations, data leaks, or incorrect provisioning.
Choosing the best authorization approach for your organization
The right authorization model depends on an organization’s security needs, scale, and operational complexity. There are three main approaches:
Coarse-Grained Authorization: This approach provides a high-level control mechanism. It’s typically easier to implement and manage. Access is often based on predefined roles or groups within the organization, making it suitable for smaller companies or less complex systems where broad access levels are sufficient.
Fine-Grained Authorization: Here, control is much more detailed. Access can be tailored to the individual level, allowing for specific permissions to be granted for particular resources or actions. It suits dynamic and large-scale environments, where access policies need to reflect detailed business rules and compliance requirements.
Hybrid Authorization: A combination of both, this approach balances ease of management with tailored access. It might involve setting coarse-grained roles with some fine-grained rules for sensitive operations, providing flexibility and control where needed.
When deciding on the best authorization model for your organization, take into consideration factors such as:
Sensitivity of controlled data
Necessity of compliance with regulations
Complexity of user roles within your system
Potential need for scalability
Fine-grained authorization is often the choice for organizations that need precise access control and expect their requirements to change.
Criteria | Fine-Grained Authorization | Coarse-Grained Authorization |
|---|---|---|
Granularity | Offers a high level of granularity, allowing for precise control over individual actions or data elements. | Provides a broader, more generalized control, often based on roles or high-level permissions. |
Use Cases | Ideal for scenarios requiring detailed control, such as financial transactions, healthcare records, or intellectual property access. | Suited for situations where simplicity and efficiency are prioritized, such as general employee access levels or public-facing information. |
Flexibility | Offers a high degree of flexibility in defining specific access rights for different users or roles. | Provides less flexibility as permissions are predefined based on roles, limiting customization for individual users. |
User Experience | Offers a more tailored user experience with users having precisely the permissions they need for their roles. | Provides a simplified user experience by grouping users into roles, reducing the need for individual permission management. |
Security | Enhances security by limiting access to only necessary actions or data, reducing the risk of unauthorized activities. | Maintains security through predefined roles but may have a slightly higher risk of over-permissioned users. |
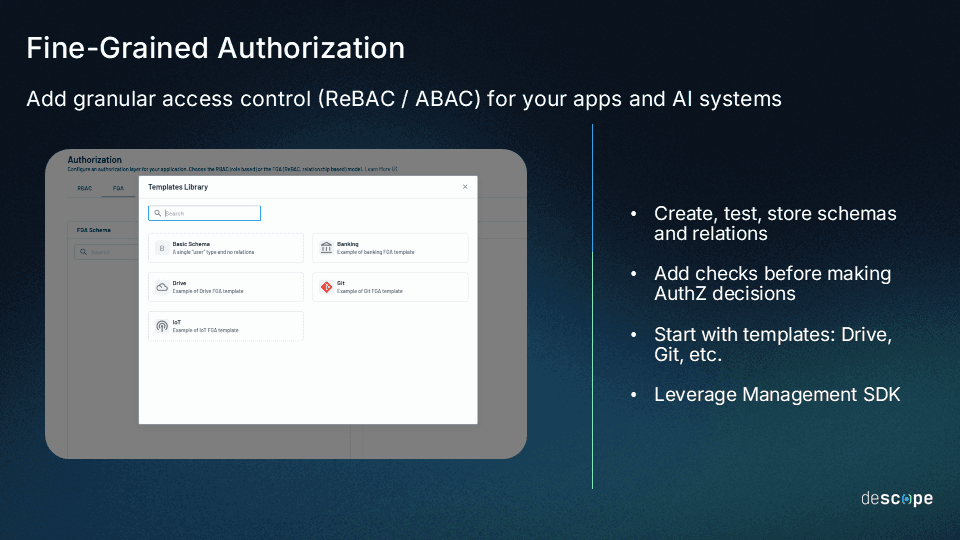
Fine-grained authorization with Descope
Adding authorization to a B2B app can be complex and time-consuming. Thinking about tenants, roles, relationships, and permissions diverts developers from other business-critical initiatives.
Descope helps developers build secure authentication and user journeys for their apps. Descope’s drag-and-drop workflows, SDKs, and APIs abstract away the complexity of authentication so developers can spend time building their core product. B2B app builders can also use Descope to add RBAC, ReBAC, and ABAC to their app easily, with roles created at the project level or for an individual tenant. Learn more in the authorization docs.
Sign up for a “Free Forever” Descope account to get started, or schedule time with our auth experts if you have any questions.